
Countersign
Kill switch + spend guard for AI agents that spend money, across every wallet vendor at once.
Runs on your machine from its package; the steps are below.
What it does
- Reads
- Writes
- High impact
At most: moves money, runs code or commands, deletes data, or sends messages for you.
What it costs
FreeOdel charges nothing per call. The publisher may charge for its own service.
Runs locally over stdio
This server isn't hosted — your MCP client launches it from a package registry. Use one of the commands below, or drop the config into your client (e.g. Claude Desktop).
Run
npx -y @countersign/mcp
MCP client config
{
  "mcpServers": {
    "countersign": {
      "command": "npx",
      "args": [
        "-y",
        "@countersign/mcp"
      ]
    }
  }
}
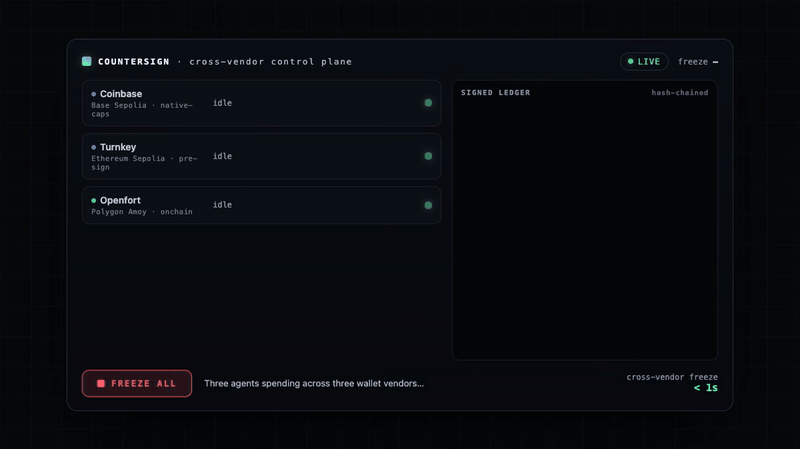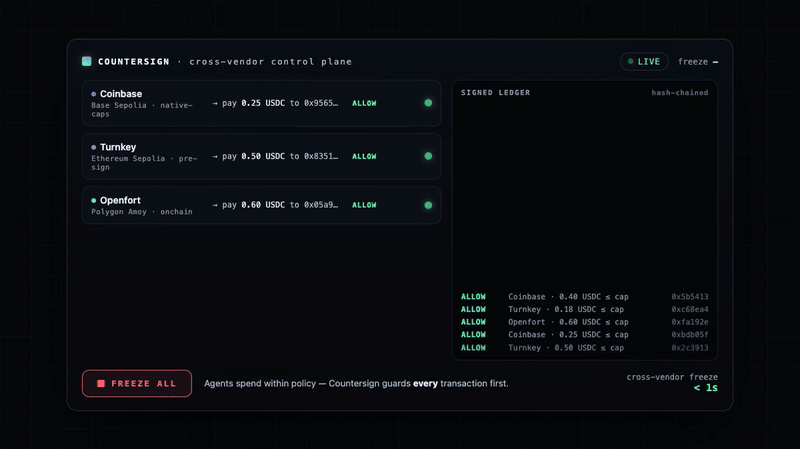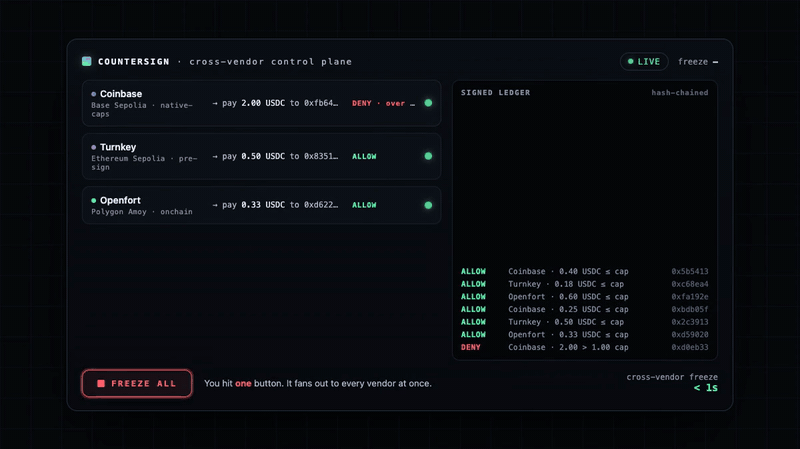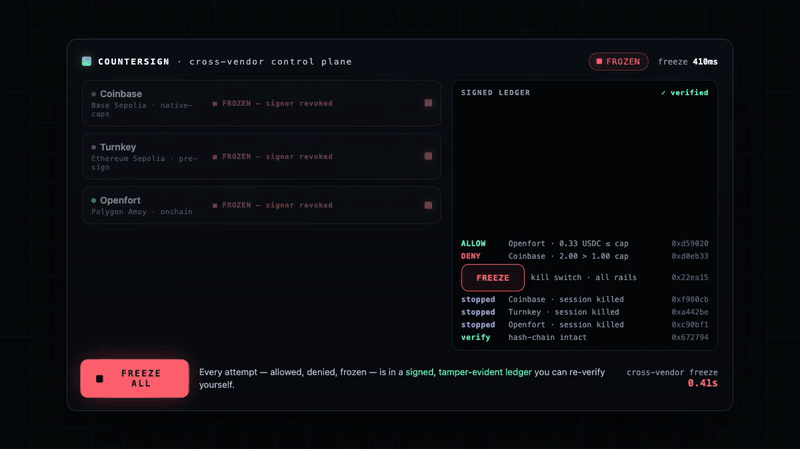
A neutral, cross-vendor control plane for AI agents that spend money. Countersign holds the policy, the freeze, and the audit ledger across multiple agent-wallet backends at once — the one thing no single wallet vendor can do, because each only governs its own rail. That aggregation is the moat.
Live version of this loop: countersign.network/demo.html · 60s video
One falsifiable test defines it: can Countersign freeze agents across many backends at once, in under a second, with a unified tamper-evident ledger of every attempt? Proven LIVE across four rails (Coinbase, Turnkey, Openfort, and a Lithic Visa card) in ~432ms on testnet.
❄️ The hosted Core is paused (2026-09-18).
app.countersign.networkis switched off: it issues no keys and existing keys no longer authenticate. These packages are unaffected — they are Apache-2.0, still published on npm, and work against a Core you run yourself. PointCOUNTERSIGN_URLat your own instance wherever this README saysapp.countersign.network.
This repository is the open-core front door — the Apache-2.0 packages you build against: the integration contract, the typed client, the MCP tools, and the x402 guard. The control-plane "brain" (the policy compiler, the hash-chained ledger, the vendor adapters, and the hosted Core) is separate and proprietary; you reach it over the network via the SDK/MCP. It was hosted at app.countersign.network, which is currently paused — self-host the Core to use these packages today.
Quickstart
Drop the kill switch + spend guard into any MCP client (Claude, Cursor, …) — one line:
// claude / cursor mcp config
{ "mcpServers": { "countersign": {
  "command": "npx", "args": ["-y", "@countersign/mcp"],
  "env": { "COUNTERSIGN_URL": "https://app.countersign.network", "COUNTERSIGN_API_KEY": "csk_…" }
}}}
Or wire it into your own agent with the SDK:
import { CountersignClient } from "@countersign/sdk";
const cs = new CountersignClient({ baseUrl, apiKey });

await cs.evaluate({ agentId, amount, asset, venue }); // may this spend happen? (allow / deny / needs_approval)
await cs.freeze();                                     // the kill switch — every backend, < 1s
Get a free testnet key at — the hosted signup is paused. Run your
own Core and issue yourself a key with app.countersign.network/startPOST /signup.
Agents paying agents? See examples/guarded-payee — the A2A/AP2
pattern where a payee advertises it is governed and the payer verifies that (and guards its own
payment) before any mandate is signed.
Packages (this repo — all Apache-2.0)
| Package | Role |
|---|---|
@countersign/core | the EnforcementProvider interface, branded ids, the unified policy schema, the fail-closed freeze controller — the integration contract every backend implements |
@countersign/api-contract | OpenAPI + typed REST/ws schema — the single source of truth for the Client↔Core wire interface |
@countersign/sdk | typed client over the Core API + live ledger subscribe |
@countersign/mcp | Countersign as MCP tools — kill switch + spend guard inside any MCP client |
@countersign/x402 | govern x402 (HTTP-402 machine payments) — guard a payment before it pays |
@countersign/verify | verify a ledger entry offline — hash chain, RFC 6962 Merkle inclusion, Ed25519 signatures |
@countersign/ap2 | govern AP2 (Agent Payments Protocol) — guard an agent-payment mandate before it executes |
The proprietary brain (policy compiler to each backend's native controls, ledger, Coinbase / Turnkey / Openfort / Lithic adapters, the hosted Core) lives in a separate private repository.
Prime directives (invariants)
- Don't build cryptography — integrate vendor MPC/TEE; session keys, never master keys.
- Build the layer above the wallets; cross-vendor aggregation is the product.
- Fail-closed: no decision / no backend response ⇒ the transaction does not execute.
- Backend-agnostic core; no vendor logic leaks past the
EnforcementProviderinterface. - Append-only, hash-chained ledger is the source of truth.
- Testnet only — mainnet follows a third-party security audit.
Links
- Home: https://countersign.network · Hosted Core: paused since 2026-09-18
- npm:
@countersign/sdk·@countersign/mcp·@countersign/x402·@countersign/ap2 - Architecture:
docs/architecture.md· Security:SECURITY.md
Apache-2.0. Countersign holds policy, freeze, and a tamper-evident ledger — it never takes custody of funds.





