Netra
eBPF network observability and safe emergency control for Linux and Kubernetes.
Runs on your machine from its package; the steps are below.
What it does
- Reads
- Writes
- High impact
Not assessed yet.
What it costs
FreeOdel charges nothing per call. The publisher may charge for its own service.
Runs locally over stdio
This server isn't hosted — your MCP client launches it from a package registry. Use one of the commands below, or drop the config into your client (e.g. Claude Desktop).
Run
docker run -i --rm ghcr.io/zyvorai/netra-mcp:0.32.0
MCP client config
{
  "mcpServers": {
    "netra": {
      "command": "docker",
      "args": [
        "run",
        "-i",
        "--rm",
        "ghcr.io/zyvorai/netra-mcp:0.32.0"
      ]
    }
  }
}Netra





See every packet's story. Contain the bad ones. Let go automatically.
Standalone eBPF network observability and emergency network control for Linux/Kubernetes — with optional Cilium + Hubble enrichment. Kernel drop attribution, path and congestion diagnostics, live packet capture, and leased deny rules that return to observe on their own, on any CNI.
Observe-first · Lease-bounded, fails open · No CNI required · No payload collection · 190 MCP tools
📖 Read the full docs — quickstart, architecture, security model, and a product tour.
What's new
From CHANGELOG.md (0.28.2 to 0.30.0):
| Per-second metrics (0.30.0) | Host, network, cgroup, process-group, eBPF and workload RED series every second, with anomaly detection, metric alerts, app collectors, exporters, and a link from any chart spike to the flows and drops behind it. Docs → |
| Node isolation (0.30.0) | A per-node allow-only egress filter in shadow (count what it would block) or enforce, as a standalone TCX program. Docs → |
| Security review (0.30.0) | DNS query types, versioned threat feeds with expiry, rollback and optional HTTPS refresh, deny-predicate overlap review and exact-workload incident correlation. Docs → |
| L7 metadata on current kernels (0.30.0) | TLS SNI, HTTP Host and DNS names load again on Linux 6.8+ (they were rejected by the verifier), using bpf_loop on Linux 5.17+. Docs → |
| Netlink change recorder | Which link, address, route or neighbor changed on a node, and when, across every routing table. Docs → |
| Netlink findings and alerts | Default route removed, gateway unreachable, uplink down, MTU changed, derived from the recorded changes. |
| Who made the change | An fentry on rtnetlink_rcv_msg attributes each modifying netlink request to the process that sent it. |
| BPF attachment inventory | Netra notices when its own hooks have silently gone, for example after a NIC or bond is recreated. Docs → |
| One UX contract | Dashboard and docs site follow one design contract; Apple light by default, dark one click away. |
| Stable controller certificate | tls.existingSecret serves a kubernetes.io/tls Secret so clients can pin the controller certificate. |
Why Netra
| When this happens… | Netra gives you… |
|---|---|
| Traffic disappears and nobody can say where | Kernel drop attribution: the connection, the reason, and the kernel function that dropped it |
| You need to act now, but enforcement is scary | Leased deny that reverts by itself, previewed against live traffic first |
| Your CNI is not Cilium, or you cannot change it | cgroup v2 hooks that work on any CNI, with no kernel module and no app changes |
| "The network is slow" with no evidence | TCP path diagnostics and a Congestion Map that colors every layer of the Linux network stack by its worst finding |
| A chart spiked and you need to know why | Per-second metrics with anomaly detection, where every spike links to the flows, drop reasons and captures from that window |
| You need packets from one node, now | Filtered, time-bounded live capture with a Wireshark-style layered decode, one click from a finding |
| Your AI agent should investigate without breaking things | An MCP server with 190 tools; mutations stay behind NETRA_MCP_ALLOW_MUTATIONS |
Netra does not require Cilium. The node agent owns its own programs and maps below /sys/fs/bpf/netra. If Cilium/Hubble exists, Netra can manage CiliumNetworkPolicy and display Hubble flows, but both integrations are opt-in.
Netra vs Cilium + Hubble
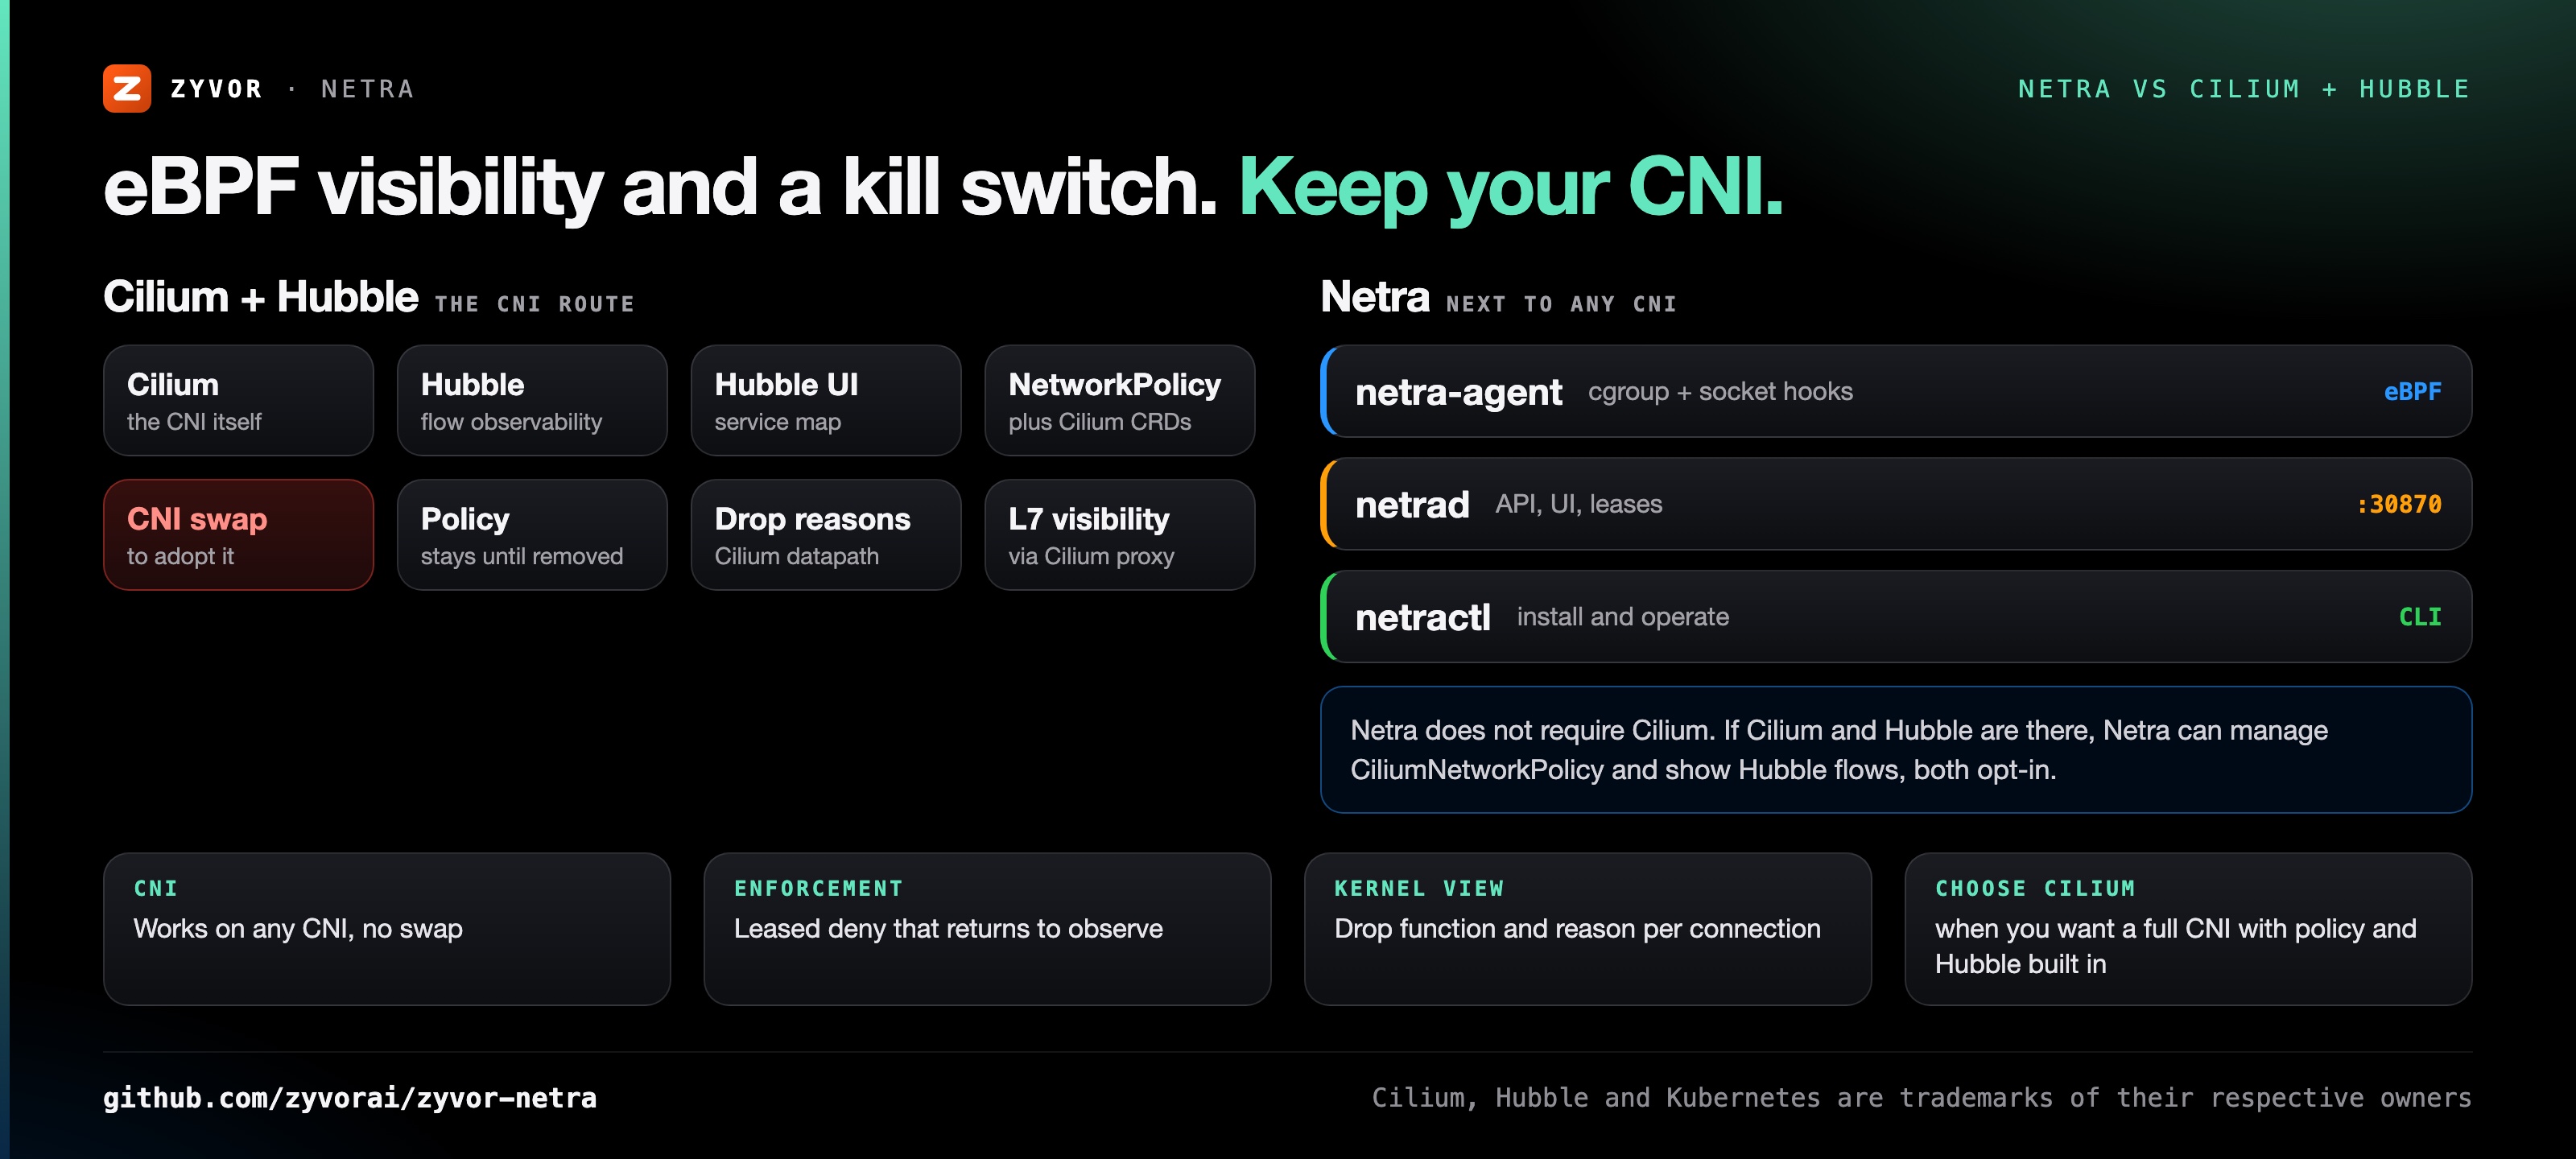
| Netra | Cilium + Hubble | |
|---|---|---|
| What it is | Observability and emergency control that runs next to your CNI | A CNI with Hubble observability built on its datapath |
| Adoption | Helm install of a controller and a node agent DaemonSet; no CNI change | Cilium becomes the cluster's CNI |
| Kernel hooks | cgroup skb, connect/sendmsg, sockops; optional kfree_skb, TCX and XDP | Cilium's own eBPF datapath |
| Enforcement model | Leased deny that returns to observe when the lease expires or the controller loses state | Network policies persist until removed |
| Drop diagnosis | Kernel drop reason and dropping function per connection, plus Drop Explain | Hubble flow verdicts and drop reasons from the Cilium datapath |
| Plain Linux hosts | The same agent and hooks | Built around Cilium-managed networking |
| Works together | Optional CiliumNetworkPolicy authoring and Hubble Relay flows | — |
| Choose Cilium + Hubble when | You want a full CNI with policy enforcement and Hubble observability built in, and can make it your CNI |
Netra never modifies or pins over Cilium-owned BPF maps, so the two can share a cluster.
See it live
Overview, the Firewall page's unified rules table and NetPol v2 allow-list, then a real in-browser VNC console connected to a running KubeVirt VM — captured against a live lab deployment, not a mockup:
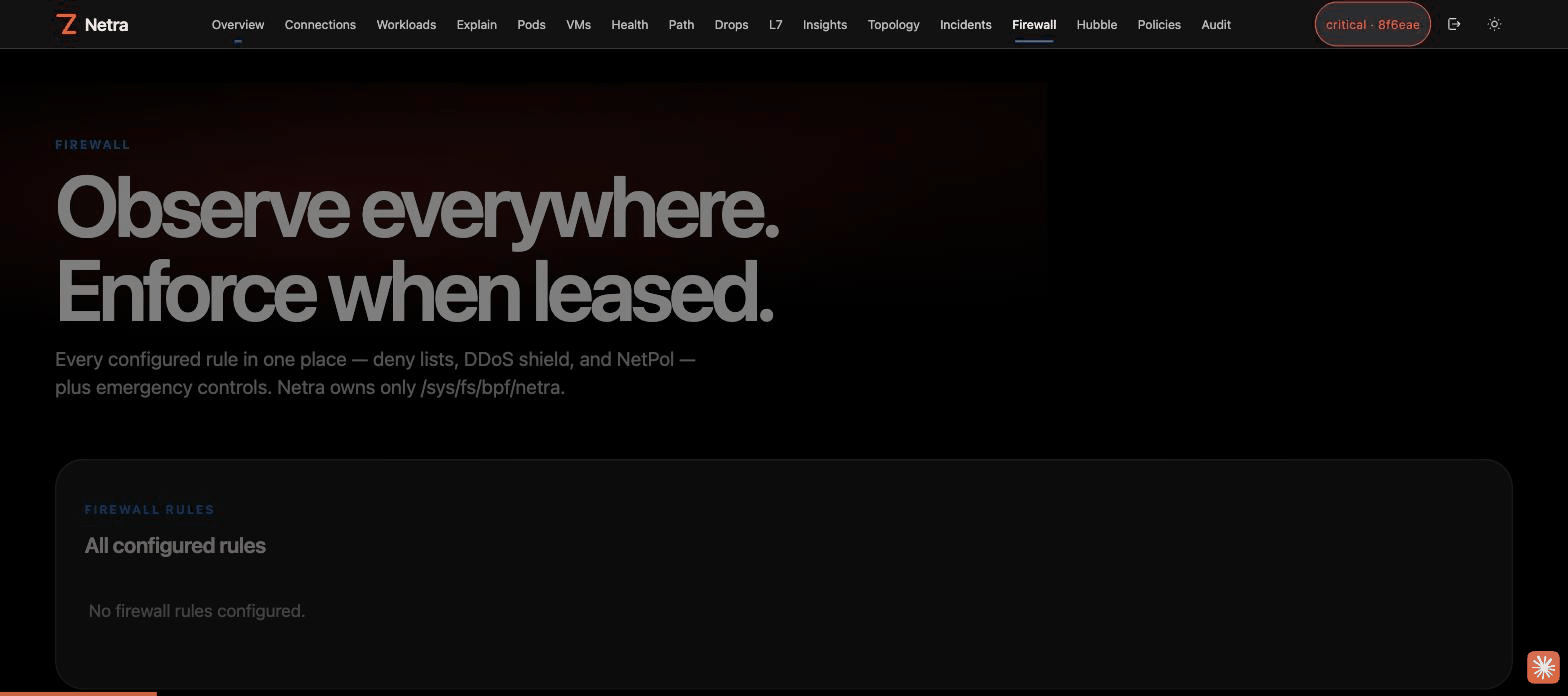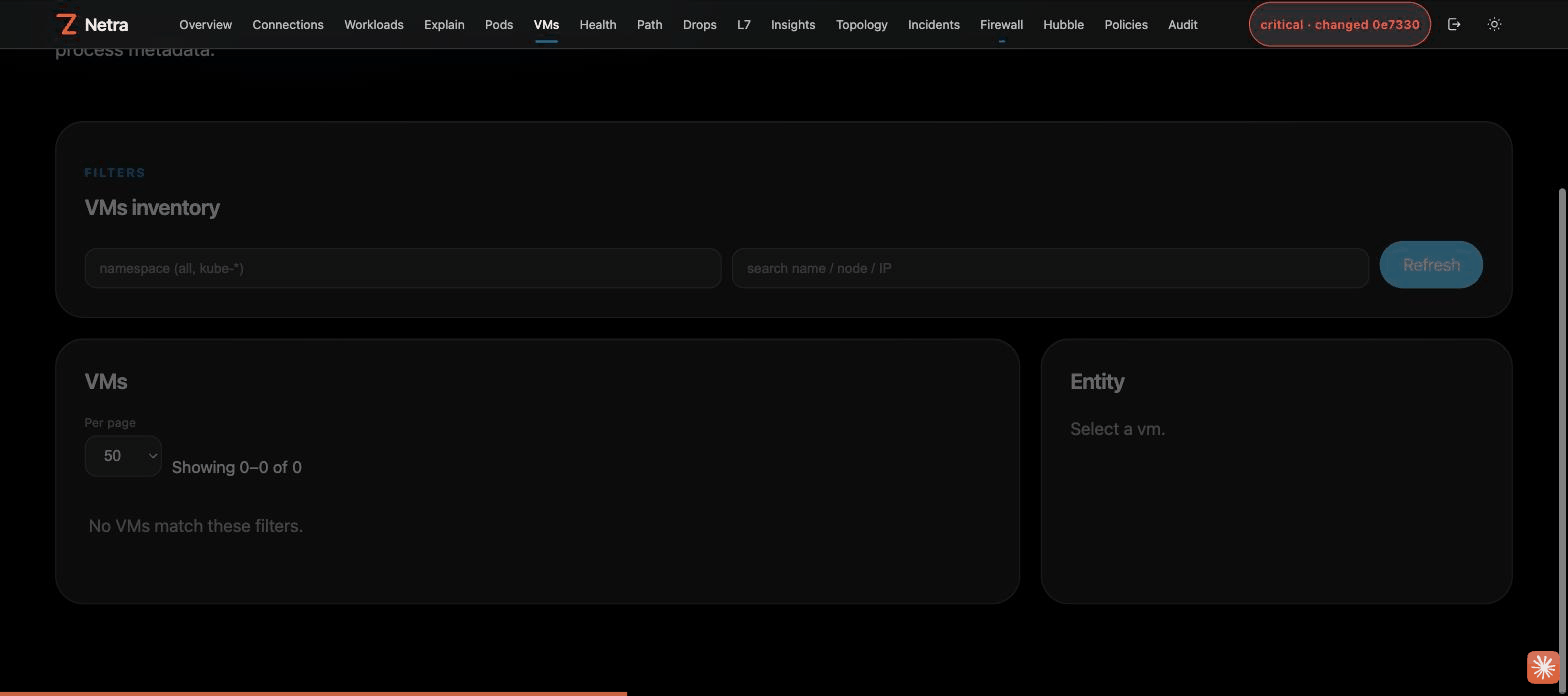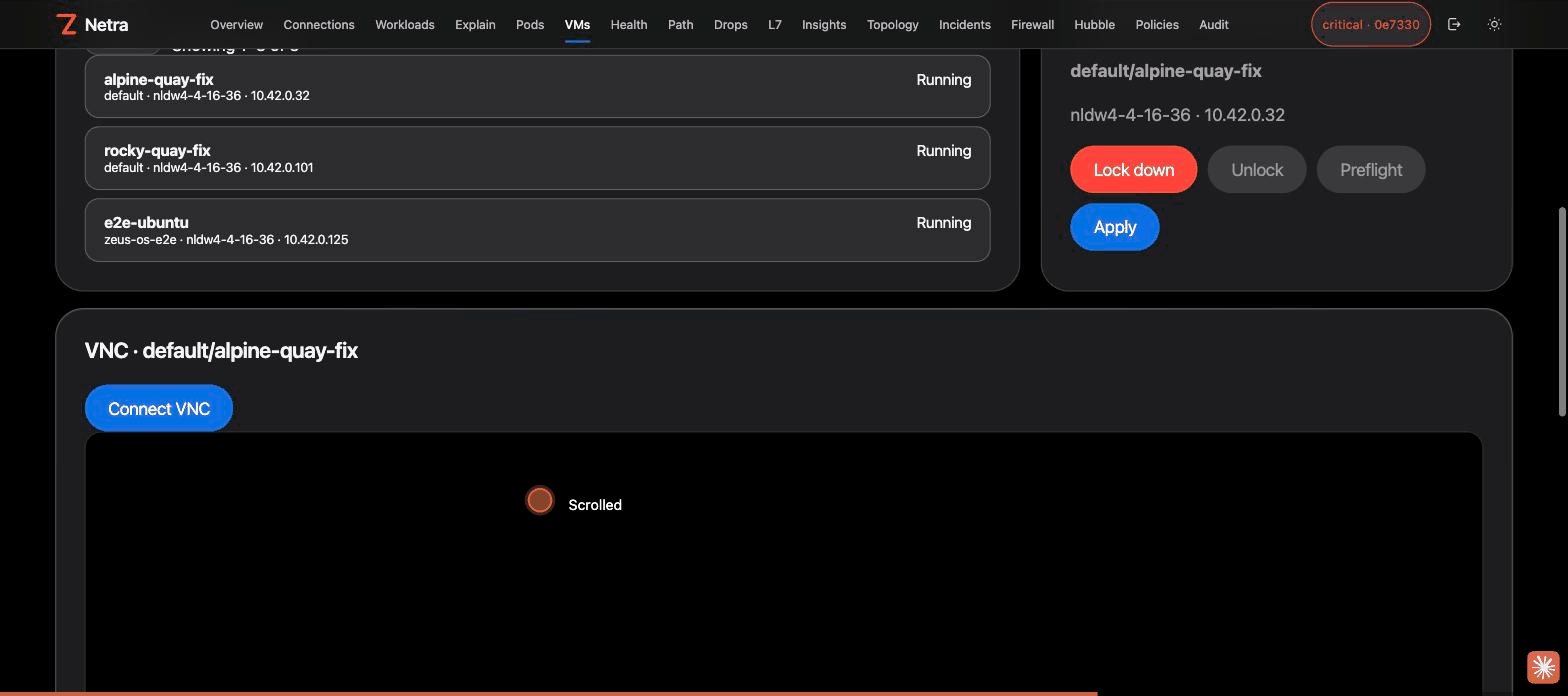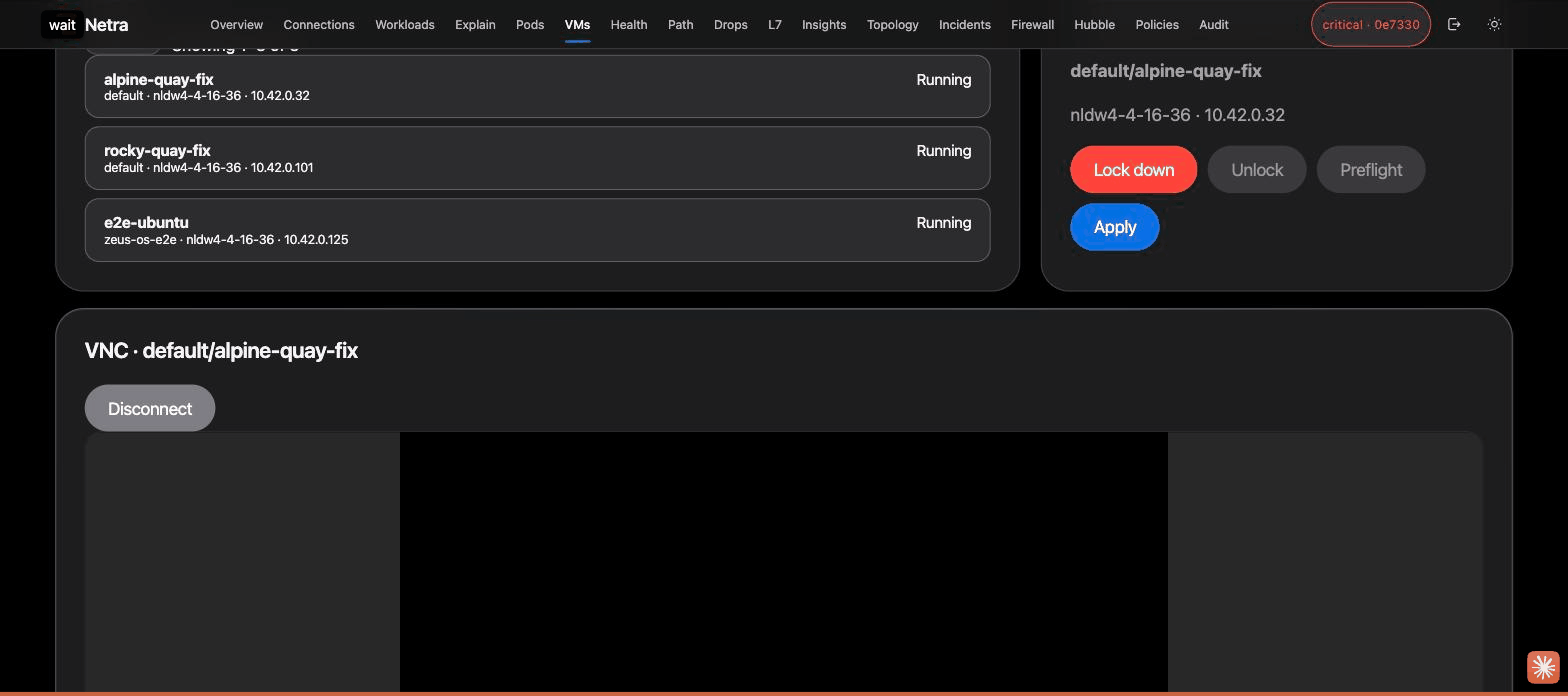
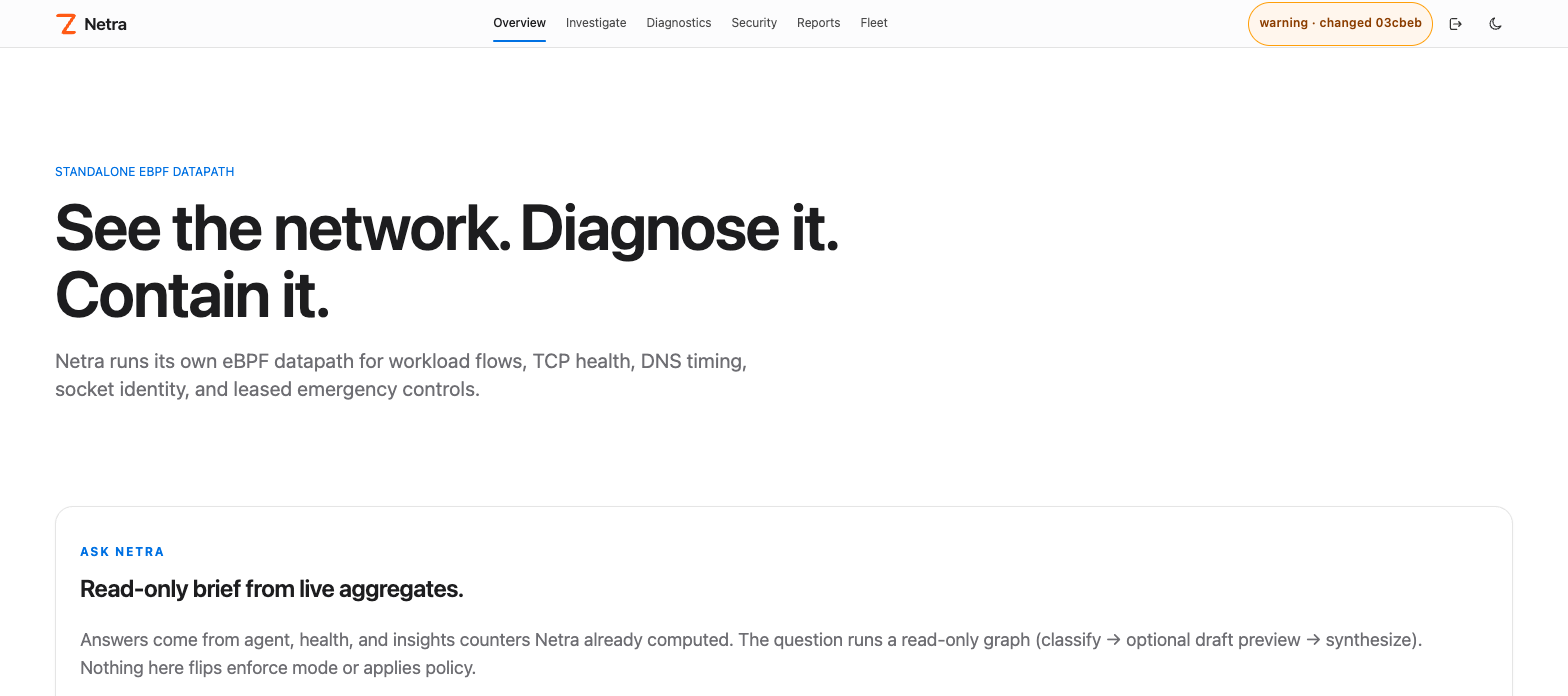
The Overview page. More screens follow in Observe, Diagnose and Contain.
How it fits together
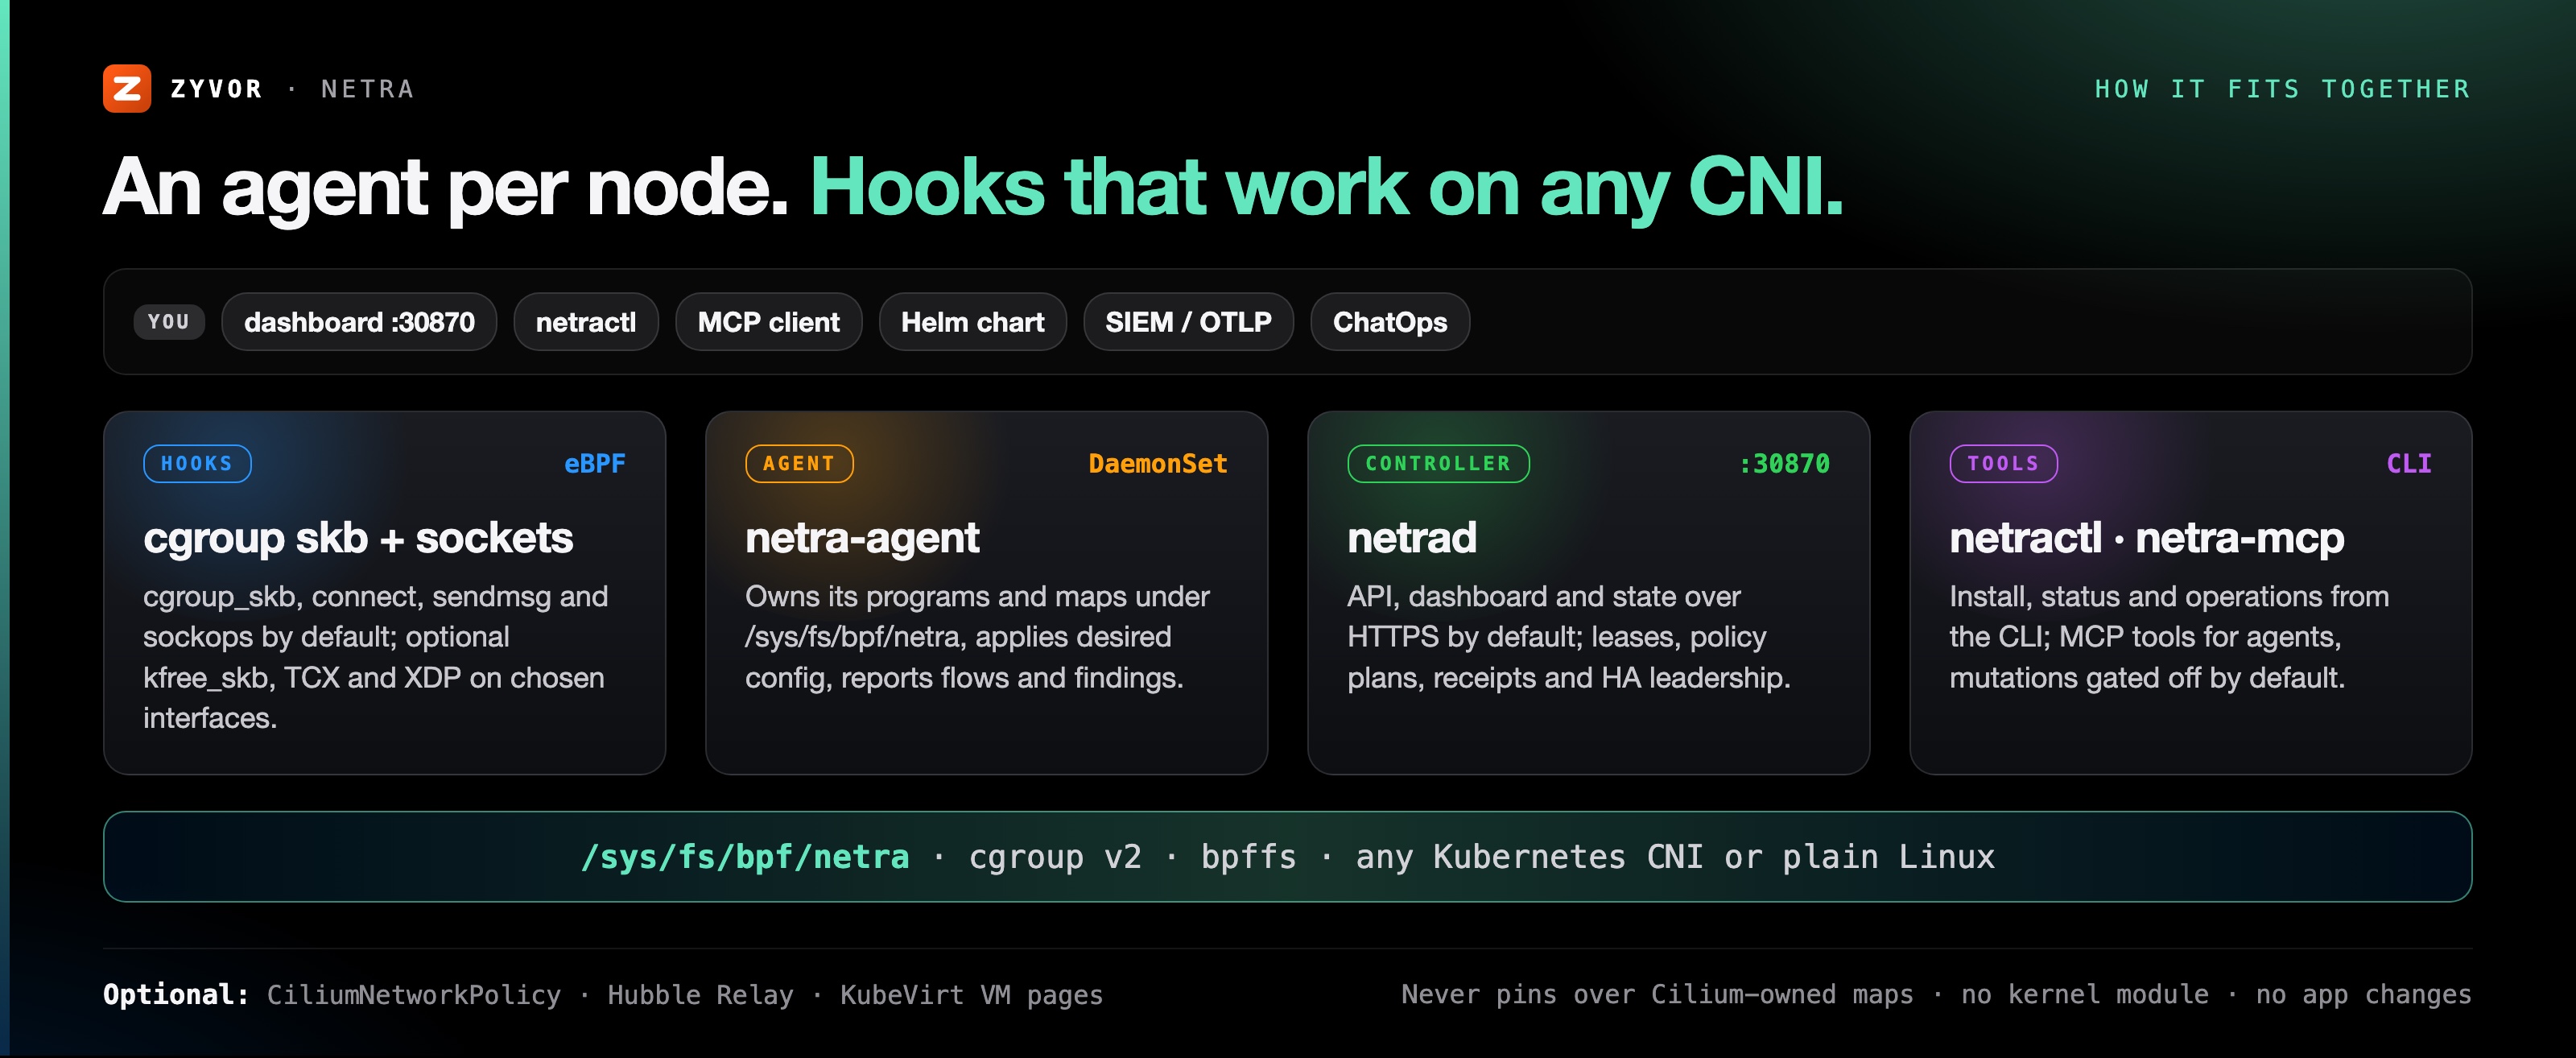
                        Browser / netractl
                               |
                               v
                    +---------------------+
                    |      netrad        |
                    | API + UI + state    |
                    +----------+----------+
                               |
                 desired config| node reports
                               v
       +------------------------------------------------+
       |          netra-agent on every Linux node      |
       |                                                |
       | cgroup skb + socket hooks       optional TCX   |
       |          |                         optional XDP |
       |          +------ Netra maps/ring buffer ------+
       |                 /sys/fs/bpf/netra             |
       +------------------------------------------------+
netrad serves HTTPS on :30870 by default. Hook model, visibility boundaries and the optional Cilium/Hubble integration: docs/architecture.md · Standalone eBPF.
Quickstart
make install                              # netractl → /usr/local/bin (or PREFIX=$HOME/.local)
netractl install --namespace netra-system # Helm install: controller + node agent DaemonSet
netractl status
Then open https://<node-ip>:30870 and sign in. The dashboard sits behind a login screen — see Signing in (the nav bar and login screen carry the Zyvor mark).
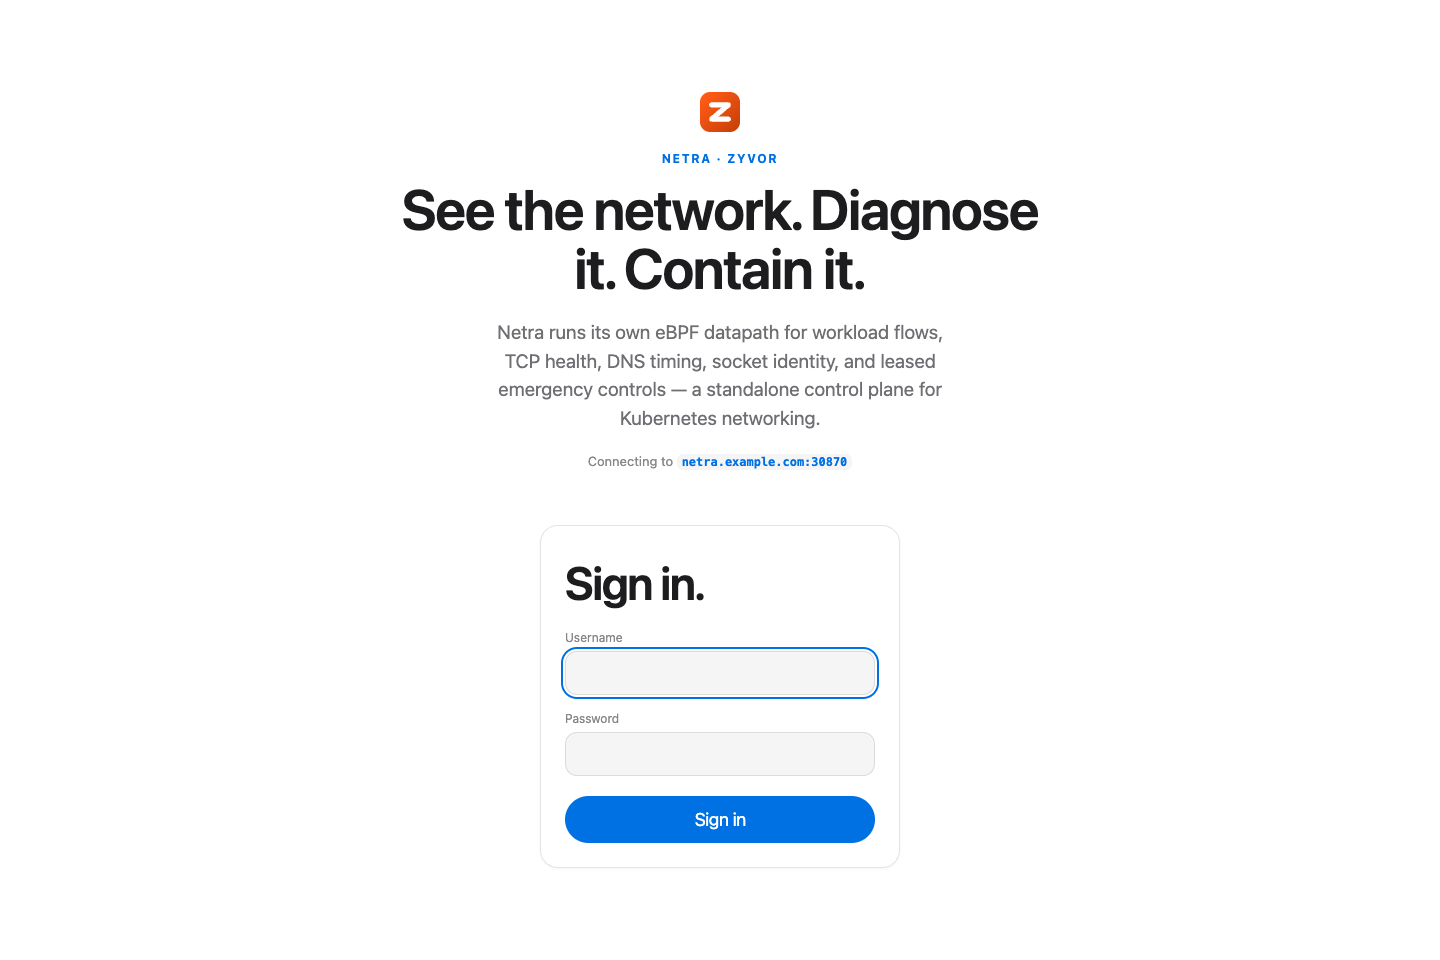
Requires Linux with cgroup v2 and bpffs; practical baseline Linux 5.8+ (TCX 6.6+). Run netra-doctor first. Full steps, Helm values, Cilium/Hubble and CLI examples: Install guide.
Observe
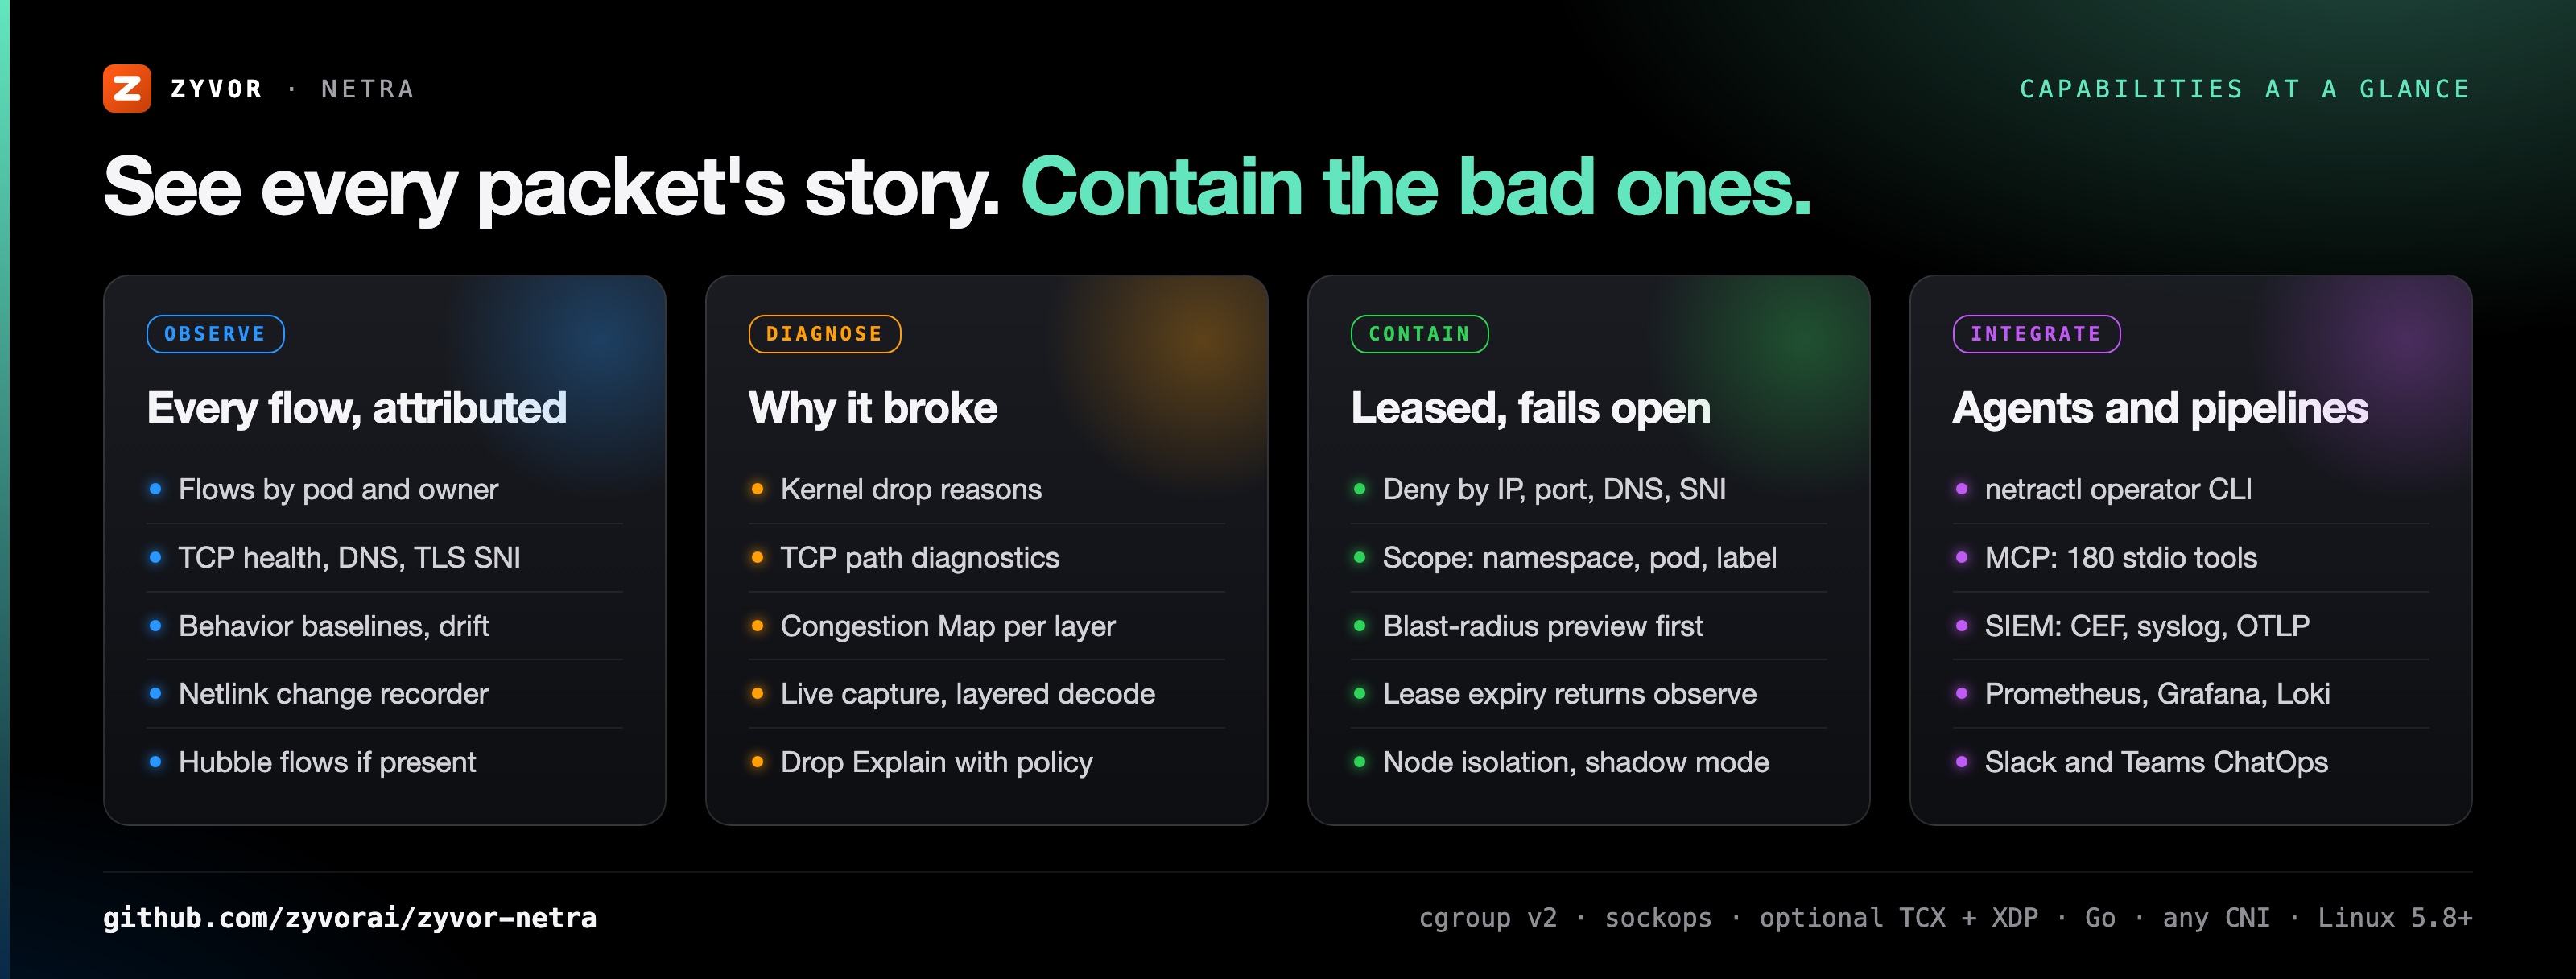
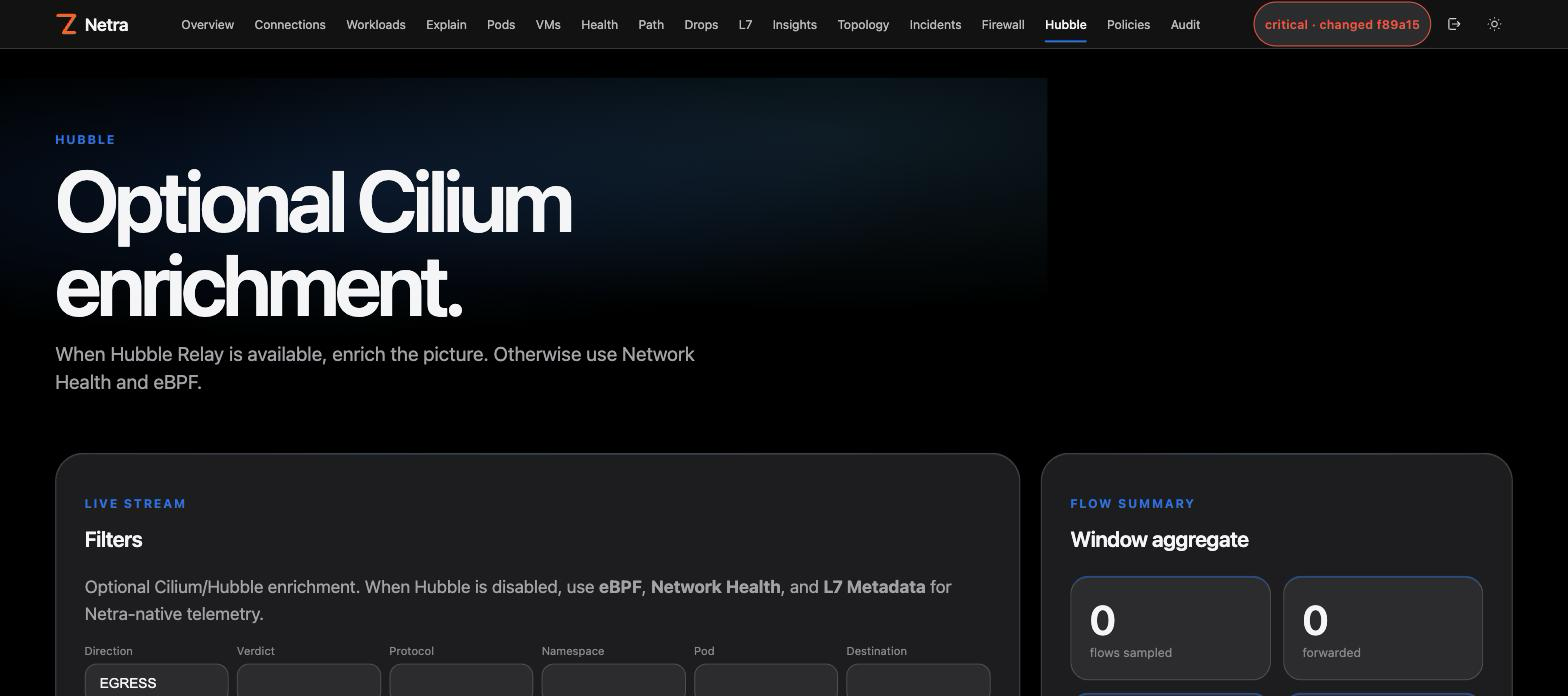
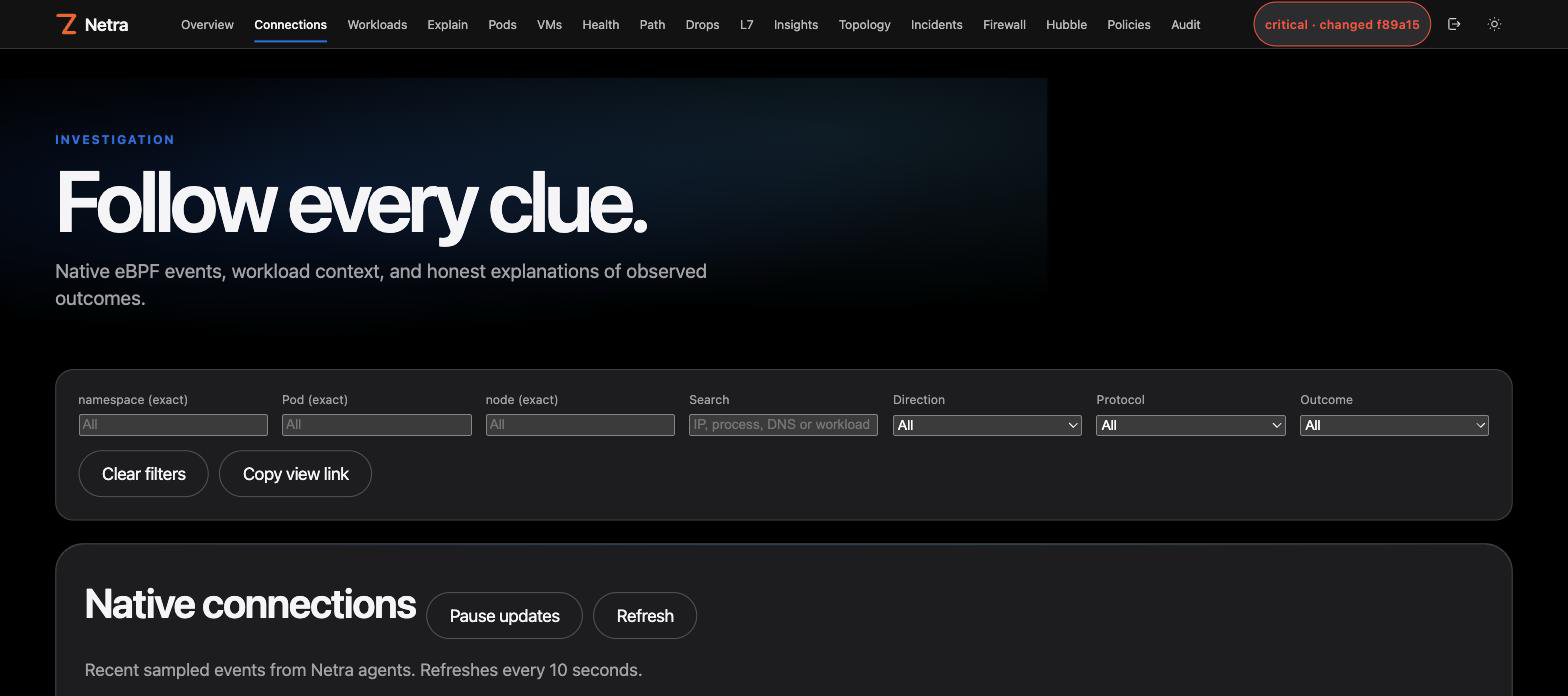
Flows with pod and owner attribution, TCP health, DNS, TLS SNI and HTTP Host metadata, behavior baselines and drift. Live Hubble flows when Cilium is present. Capabilities →
Diagnose
TCP path diagnostics measure connect latency and transport pressure per workload, plus edge-observed handshake and RTT histograms that see NAT'd flows. Path → · Edge intel →
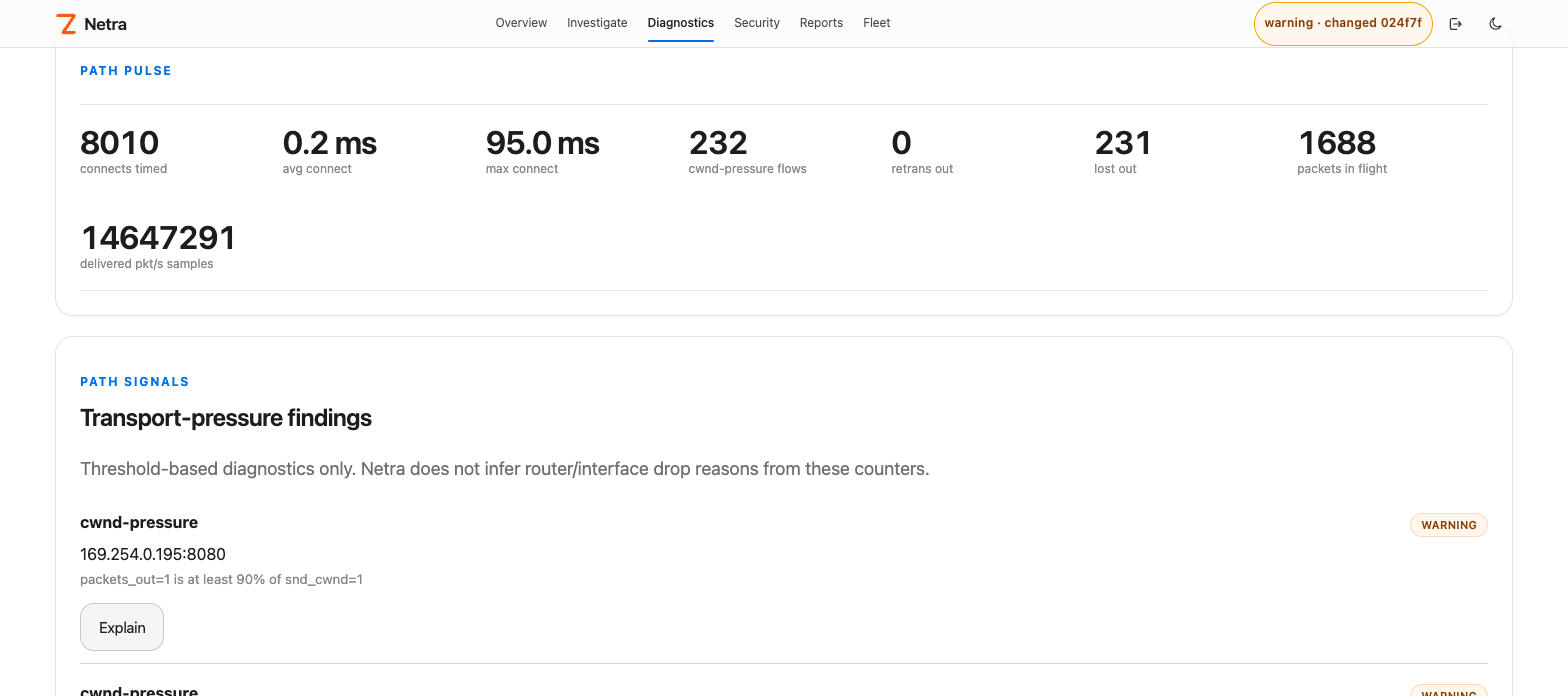
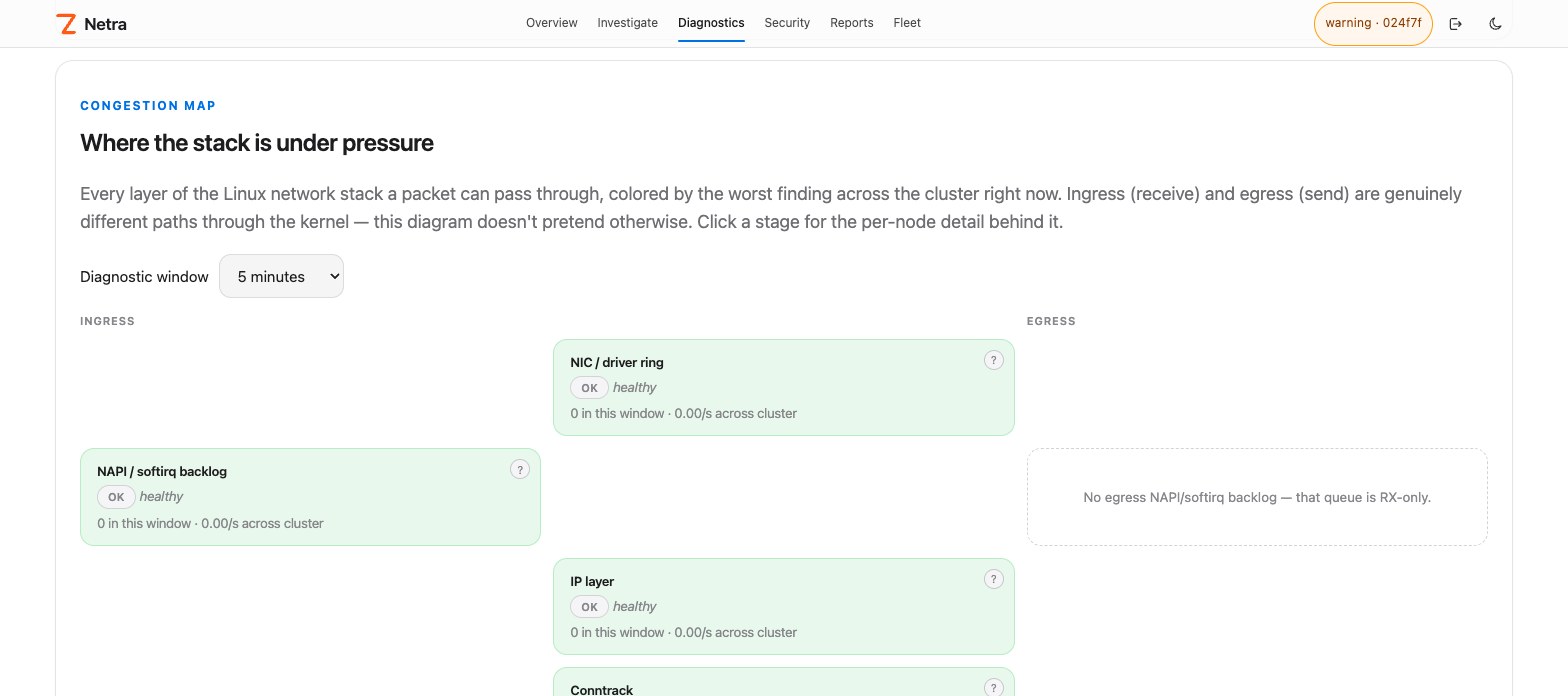
Congestion Map colors every layer of the Linux network stack by its worst finding, cluster-wide. One click jumps to a capture on the offending node. Kernel diagnostics →
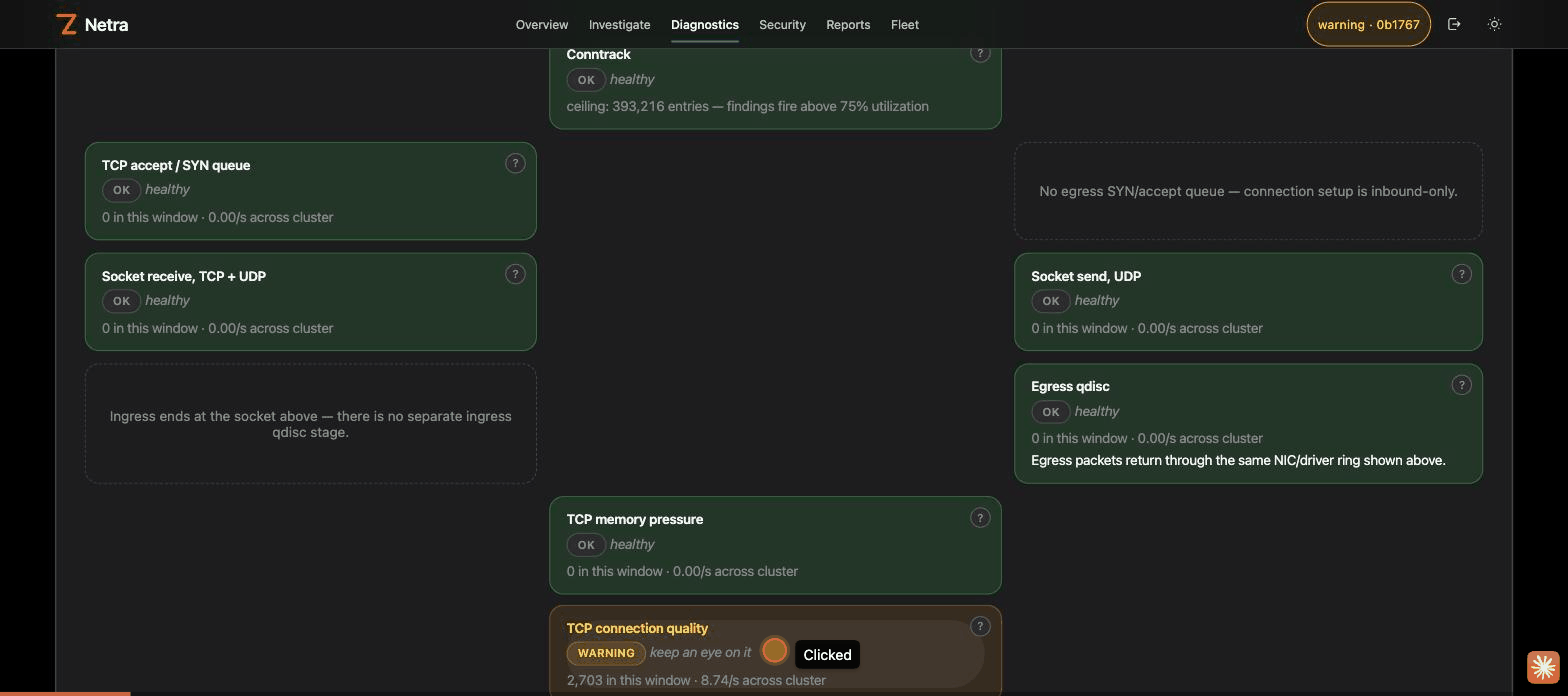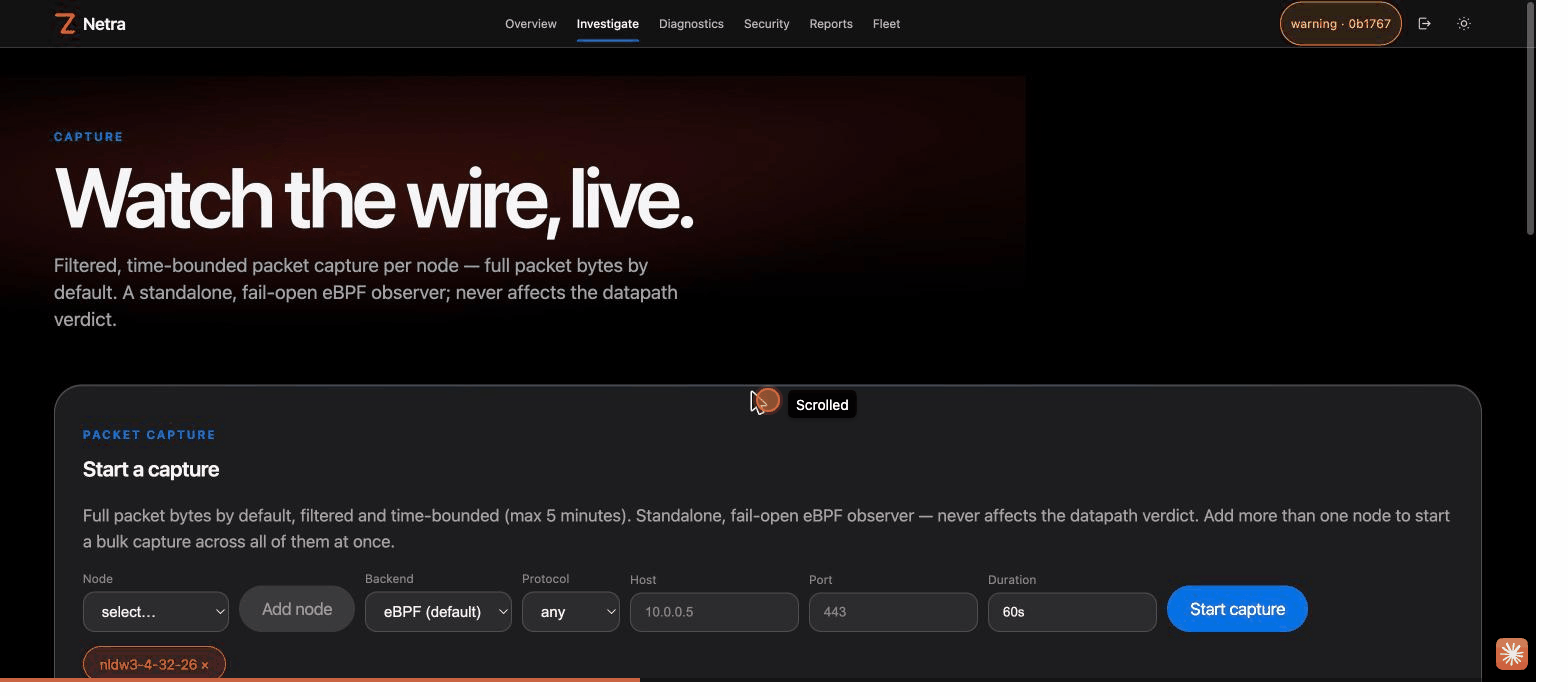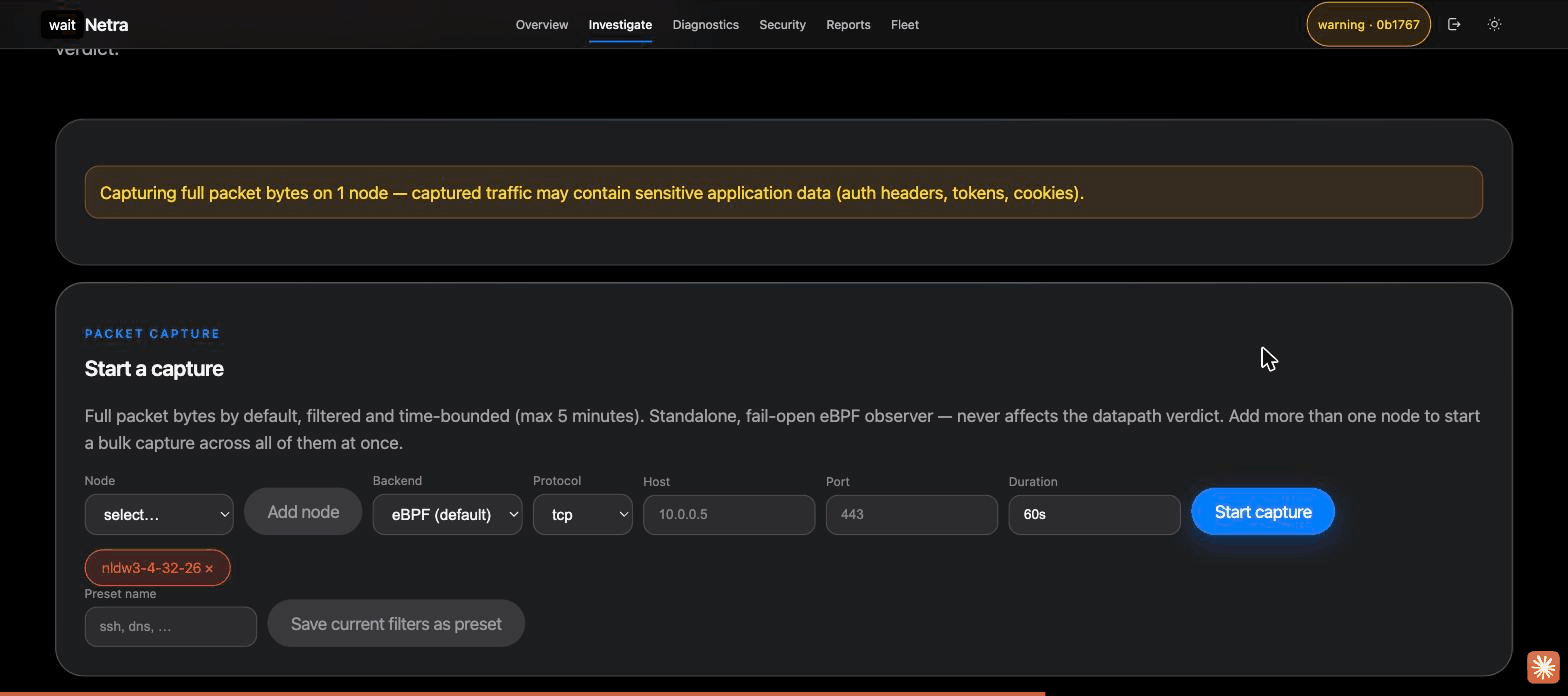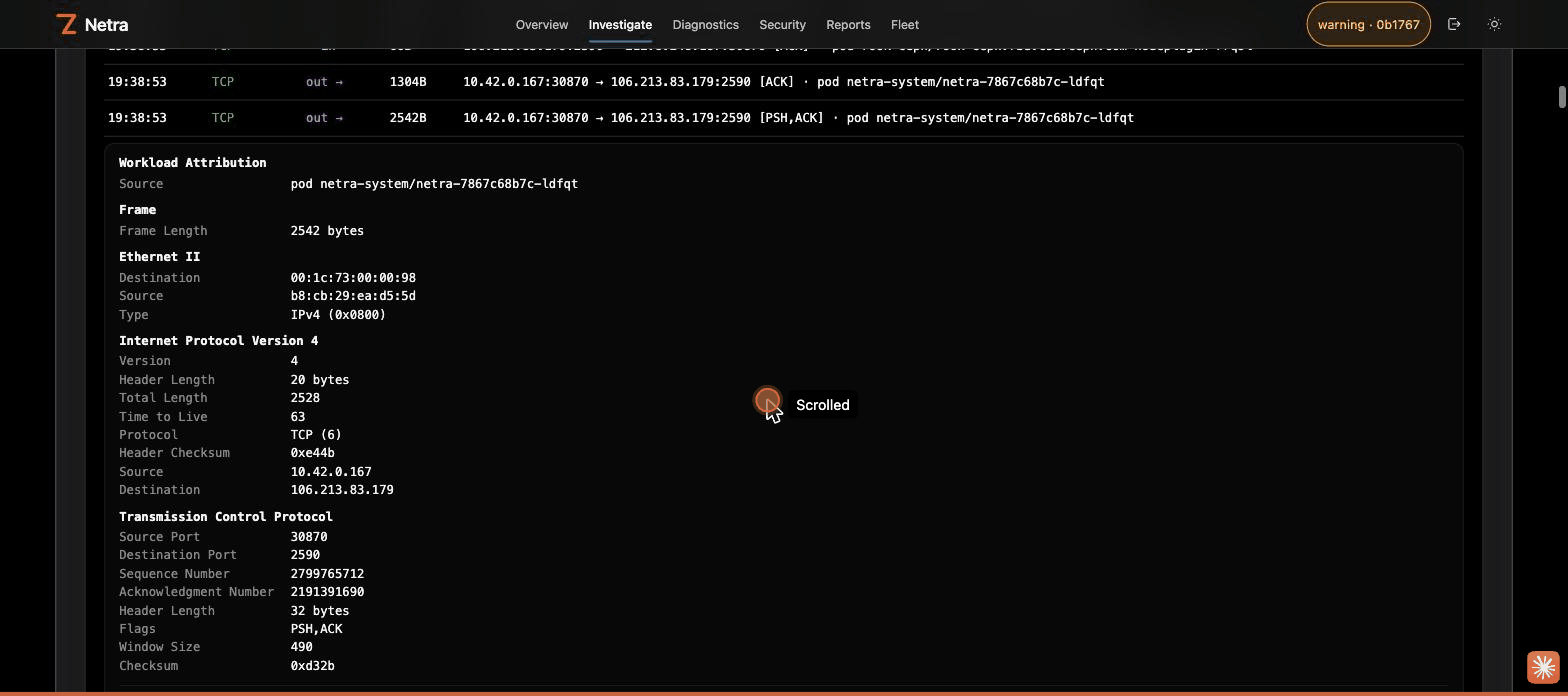
Packet Capture streams a filtered, time-bounded capture live, color-coded by protocol, with a Wireshark-style layered decode and hex dump. Opt-in auto-capture persists PCAPs on critical findings. Capture →
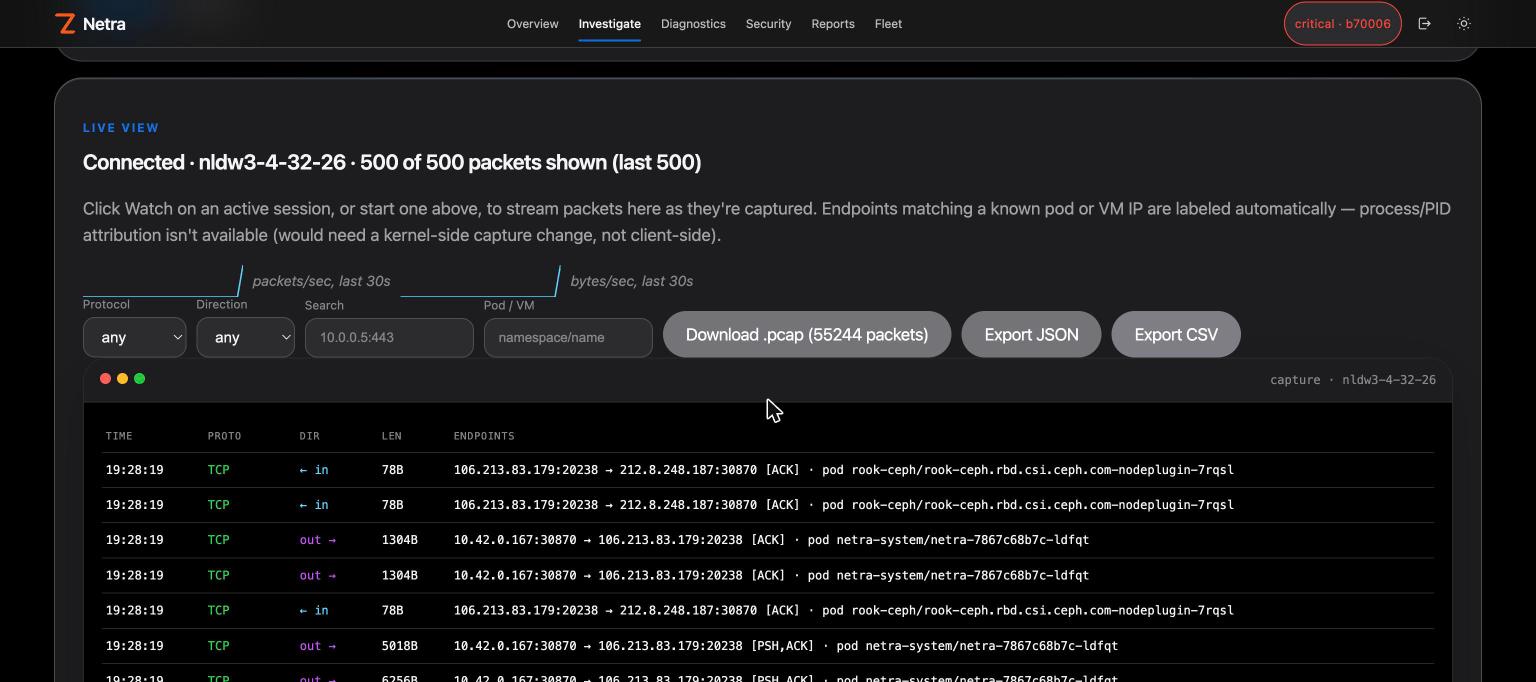
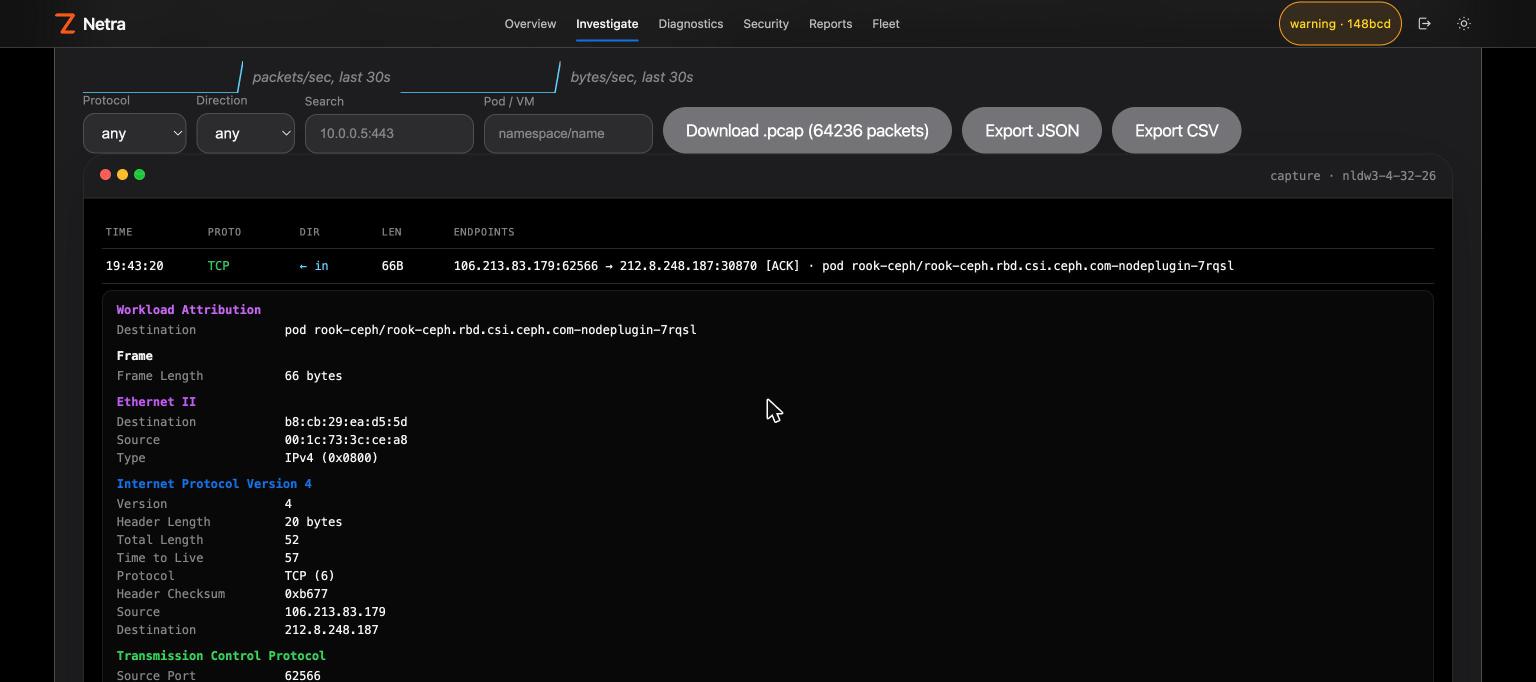
A Congestion Map finding to a live, decoded, color-coded capture on the offending node:
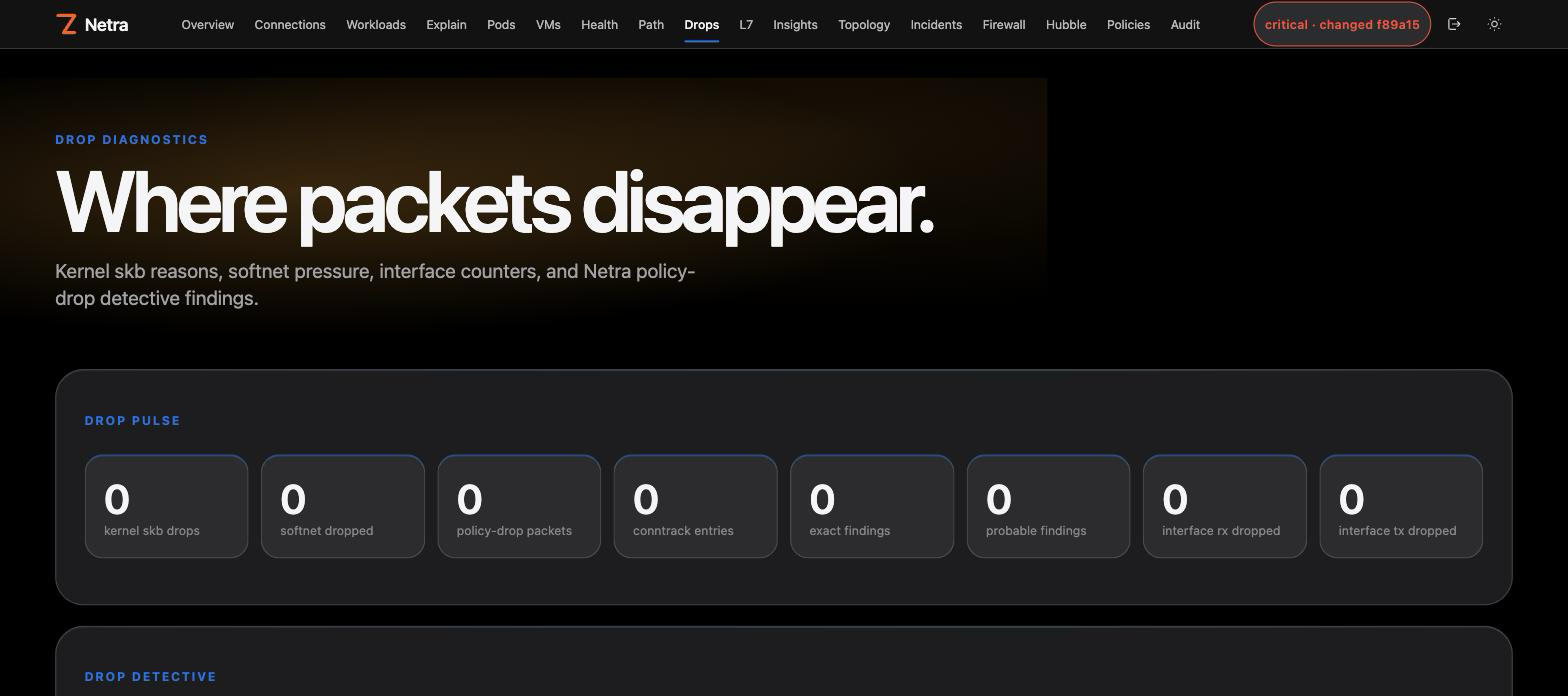
Drop Explain answers "why was this dropped?" with kernel reasons and policy context. Drop diagnostics → · Drop info →
More: DNS, ICMP, behavior and rate insights.
Monitor
Per-second metrics, zero config. Every node streams host, network stack, conntrack, cgroup, process-group, eBPF datapath and per-workload RED series to the controller, kept at 1 s for an hour, 1 min for two weeks and 1 h for a year. The Metrics page charts every context live, with an anomaly ribbon on each chart. Metrics →
- Anomaly detection on every dimension (unsupervised k-means, stdlib Go), plus "what changed here" ranking for any time range you drag across. Anomalies →
- Metric alerts with Netdata-style rules and hysteresis, over 40 built in (CPU, memory, disk, interfaces, TCP, conntrack, workload RED, eBPF drops), sent through your existing Slack, webhook or PagerDuty channels. Alerts →
- Evidence behind every chart: a spike links straight to the flows, drop reasons, TCP/DNS/HTTP boards and captures from the same window. Metrics and packets in one place.
- App collectors for nginx, Apache, HAProxy, Redis, memcached, Envoy, CoreDNS, etcd and any Prometheus endpoint, with optional discovery. Apps →
- Export to Prometheus remote write, OTLP or Graphite, and a read-only fleet roll-up across clusters.
Collectors are read-only, process groups use the kernel comm only (never argv or environment), and alerts never touch enforcement.
Contain
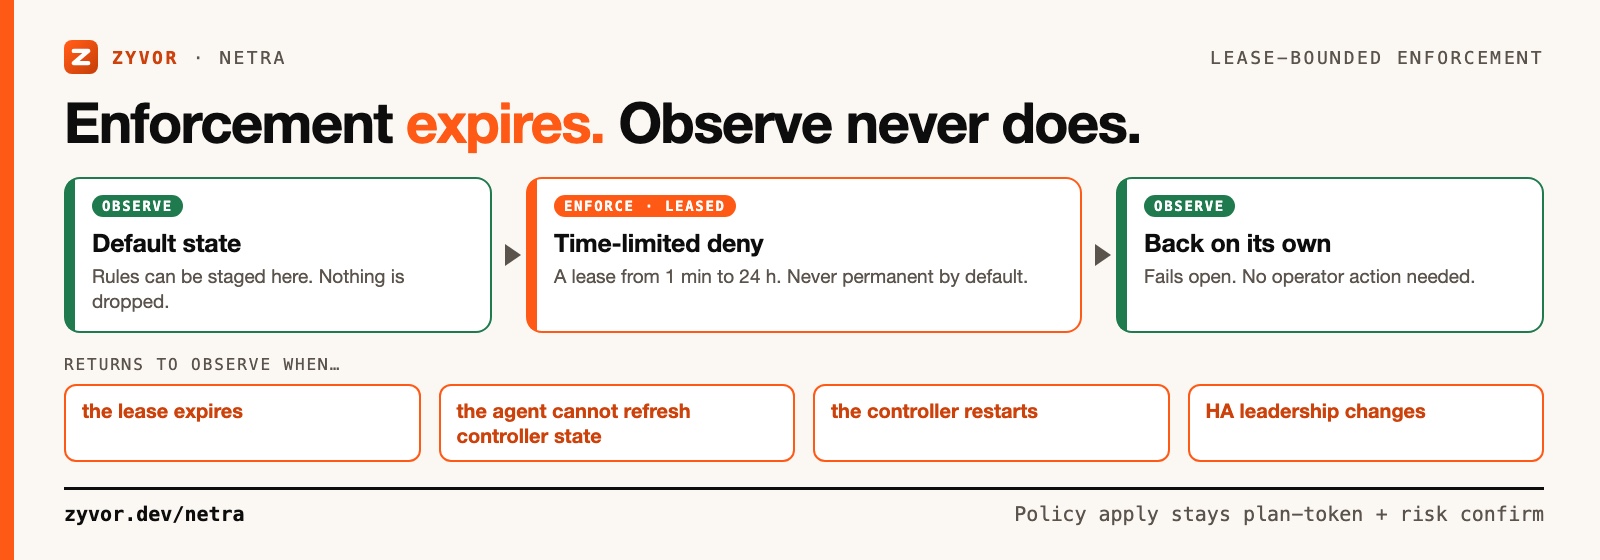
Deny by IP, CIDR, port, DNS name, TLS SNI, UID or process, scoped to a namespace, pod, owner or label. Preview the blast radius first. Policy apply stays plan-token + risk confirm. Firewall page →
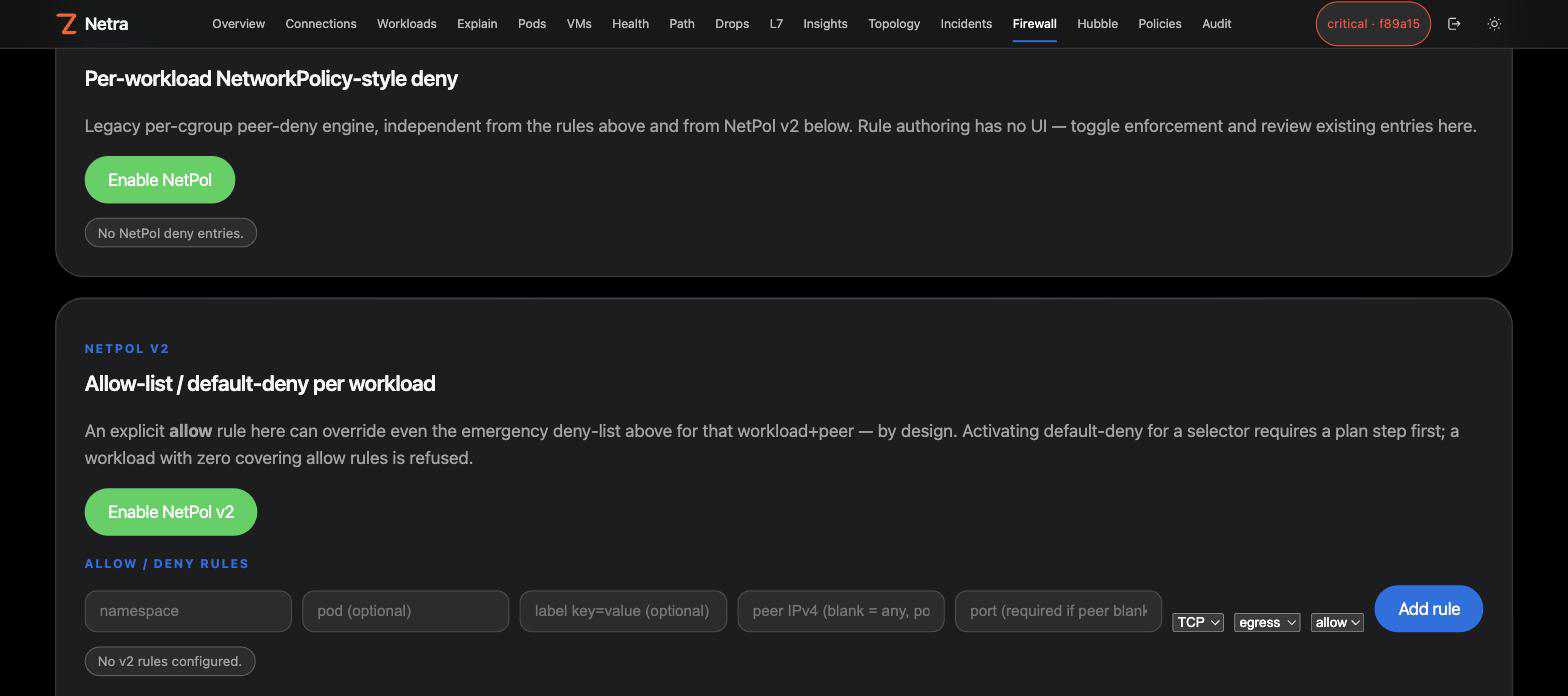
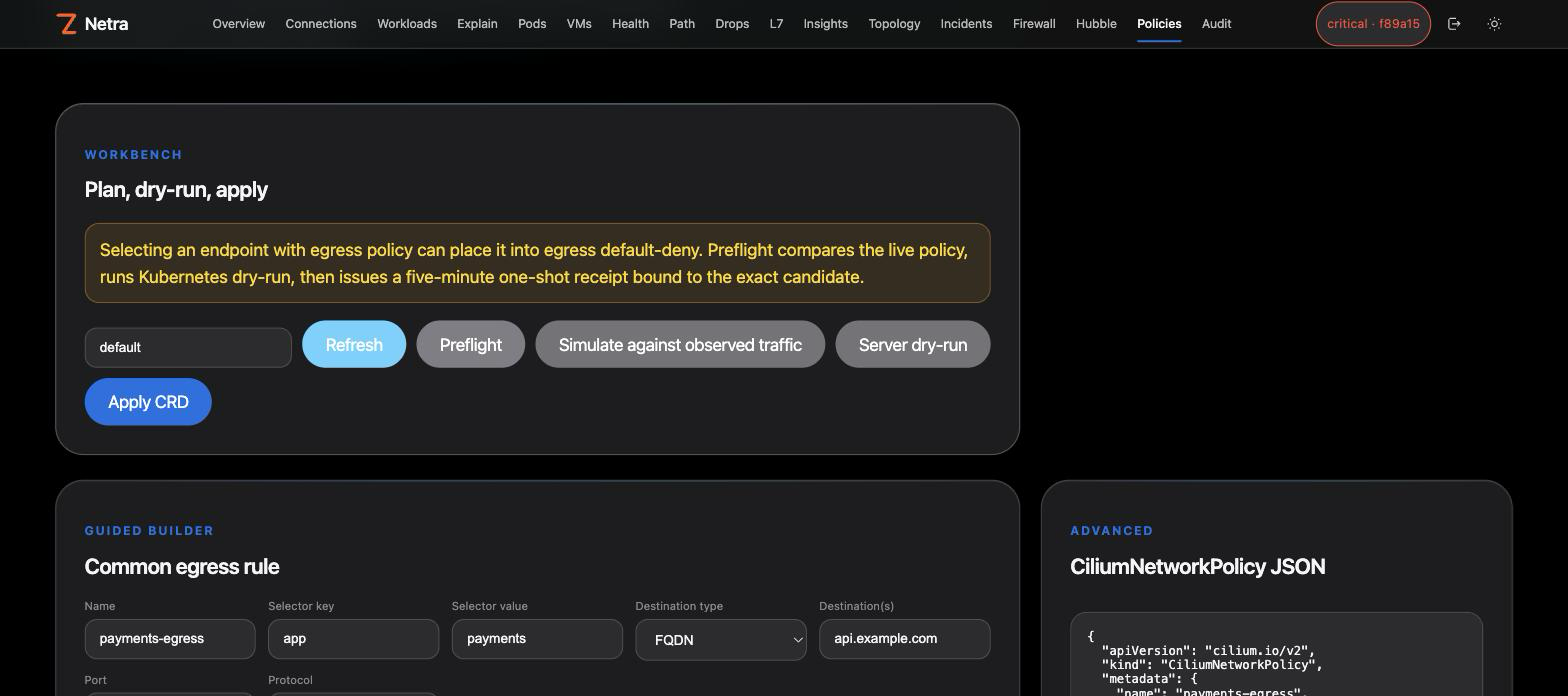
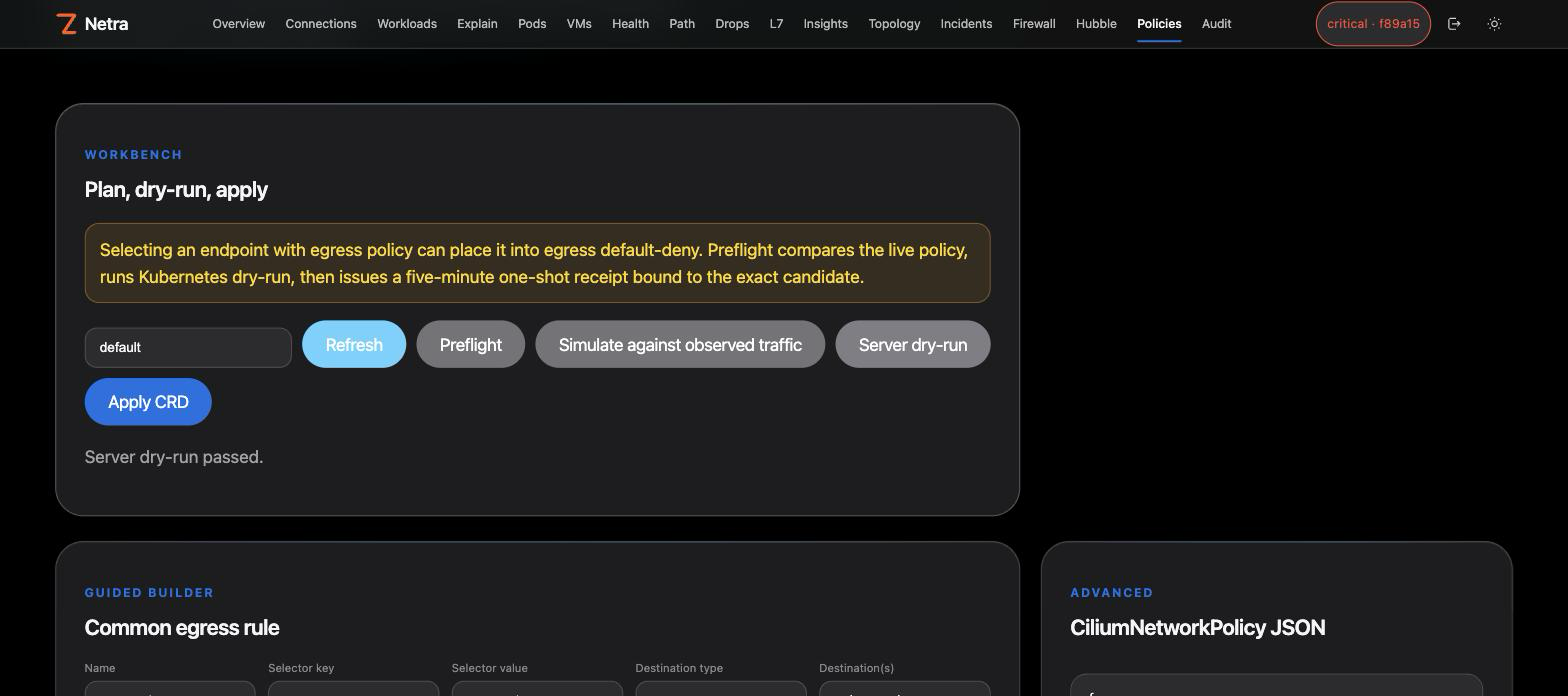
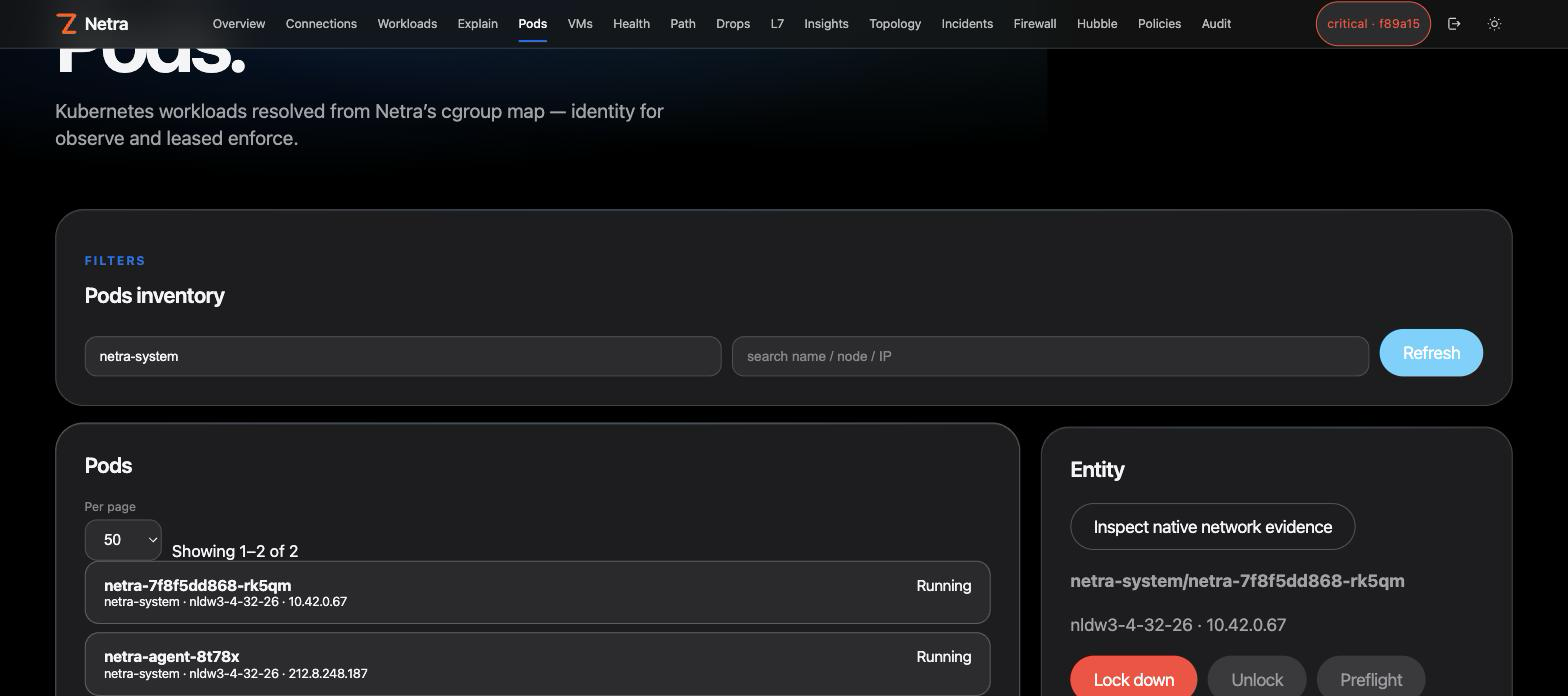
With Cilium enabled, Pods and VMs get one-click lock down / unlock through the same plan → receipt → apply path:
Safe by design
| Promise | What it means |
|---|---|
| Observe-first | Rules can be staged while observing. Nothing is dropped until you enforce |
| Leased enforcement | Returns to observe when the lease expires, the agent cannot refresh controller state, the controller restarts, or HA leadership changes |
| No payloads | No application payloads, no argv/cmdline, no Secret contents. Opt-in sampled sensors keep counts only |
| Gated automation | MCP mutations stay behind NETRA_MCP_ALLOW_MUTATIONS; AI endpoints are read-only |
| Cilium-safe | Never modifies or pins over Cilium-owned BPF maps |
Details: Architecture and visibility boundaries · Safety and persistence.
For AI agents and operators
netractl— the operator CLI. Docs →- Security review — DNS QTYPE, versioned threat feeds with TTL/rollback and optional HTTPS refresh, flat deny-predicate suggestions, and exact-workload security correlation. Docs →
- MCP server — 190 stdio tools (130 read, 60 opt-in mutating) for AI agents. Docs →
- MCP Registry:
io.github.zyvorai/netra(live since v0.30.1), imageghcr.io/zyvorai/netra-mcp:0.32.0. Install and use →
- MCP Registry:
- Built-in AI briefs — heuristic by default, optional OpenAI-compatible rewrite, read-only. Docs →
- Export — SIEM (CEF, syslog, JSONL, OTLP), Prometheus (scrape and remote write), Grafana, Loki, Graphite, Slack and Teams ChatOps.
Netra or PacketWolf?
Netra and PacketWolf cover the same eBPF territory from opposite directions. They are counterparts, not a wired pipeline.
| Choose Netra when… | Choose PacketWolf when… |
|---|---|
| CNI-independent observe + leased emergency kill-switch | Cilium is already the CNI of record |
| Path/Drop/Congestion diagnostics without a full platform | Full AutoPolicy / healer / operator stack |
Rules: docs/packetwolf.md · Suite placement.
Documentation map
| I want to… | Read |
|---|---|
| See everything Netra observes and controls | Capabilities · Feature catalog |
| Understand diagnostics | Diagnostics overview |
| Monitor nodes and workloads per second | Metrics · Metric alerts · Anomaly detection · App collectors |
| Understand the hooks and architecture | Architecture · Standalone eBPF |
| Install and configure | Install guide · Helm/manifests · Host readiness |
| Operate it | netractl · High availability |
| Browse the code | Repository layout · CI |
| Evaluate it as a buyer | Buyers guide · Brochure and PDFs · Resources |
Maturity
Netra's latest release is 0.32.0 (CHANGELOG.md). Shipped observe and leased-control surfaces are GA. The table below says what runs by default versus what stays opt-in for privacy or safety (architecture):
| Area | Status |
|---|---|
| cgroup skb ingress/egress, connect/sendmsg, sockops hooks | GA (default) |
kfree_skb drop reasons, TCX, XDP | GA (optional attach), on selected interfaces |
| Enforcement | GA — observe by default; leased enforce returns to observe |
| TLS SNI, HTTP Host, DNS names and query types | GA (default, NETRA_L7=auto), Linux 5.17+; dropped on older kernels |
| TLS fingerprints (JA3/JA4) | GA (default, agent.tlsfp: auto) |
| DNS anomaly detect / scan detect | GA (default); observe-only |
| Per-second metrics, anomalies, metric alerts | GA (default, NETRA_METRICS_ENABLED); alerts only notify |
| Auto-capture on critical drops | GA (default); bounded duration/cooldown/PPS; disable with alerting.autoCapture.enabled=false |
| Auto-mitigate (volumetric) | GA (default); acts only under an active enforce lease; fails open |
| Node isolation | GA — loaded (agent.nodeIsolation: auto), inert until a per-node policy is set; shadow or enforce (leased) |
| Security review, threat-feed history and rollback | GA (read-only); HTTPS feed refresh only when NETRA_INTEL_SOURCE_URL is set |
| Historical deny preview (flow history) | GA — live counters plus optional --since / flowlog window |
| Sampled L7 and TLS plaintext sensors | Opt-in (privacy), off by default |
Cilium CiliumNetworkPolicy and Hubble integration | Opt-in (cilium.enabled, hubble.enabled) |
| MCP mutating tools | Opt-in (safety, NETRA_MCP_ALLOW_MUTATIONS) |
Part of the Zyvor stack
| Product | Role next to Netra |
|---|---|
| Netra | Standalone eBPF network observability and leased emergency control, on any CNI |
| Paqtra | Next to Netra on Cilium clusters: Hubble flow tracing, drop explanations and policy preview |
| Rivora | Next to Netra: CNI-independent eBPF L4 load balancer with XDP, Maglev and BGP |
| Zorvia | Next to Netra: KubeVirt VM platform; with Cilium enabled, Netra's VMs page shows KubeVirt VMs with live flows and lock down |
| netevd | Next to Netra on hosts: netlink and eBPF network events into hook scripts and policy routing |
License
Netra is source-available under the Zyvor Production License v1.0 (SPDX LicenseRef-Zyvor-Production-1.0, also in LICENSES/).
- Free for evaluation, development, testing, research, education, non-production labs and all other non-production use.
- Production use requires an annual enterprise subscription. Plans, support levels and terms: docs/SUBSCRIPTION-MODEL.md · Enterprise pricing · Pricing · sales@zyvor.dev.
Contributions: CONTRIBUTING.md. Report vulnerabilities privately per SECURITY.md.